Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
Sep 19, 2026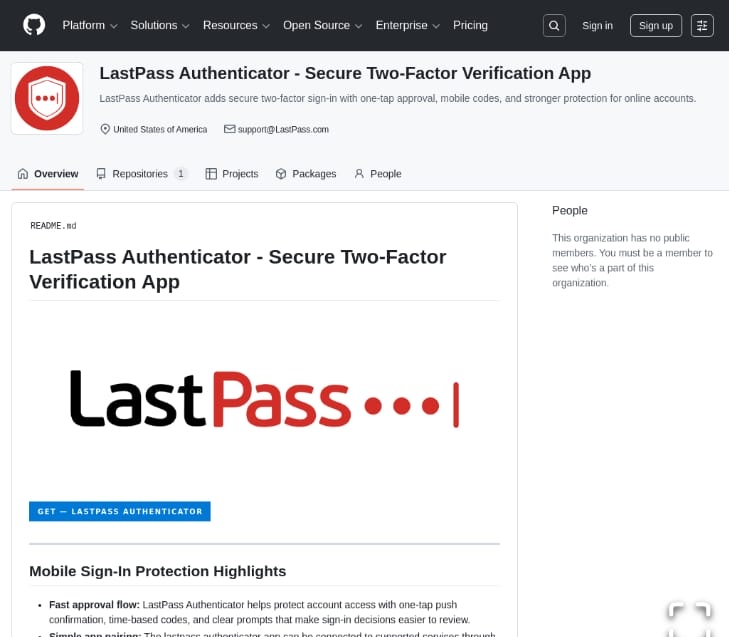
An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel. The installer inside the archives is a copy of the legitimate Microsoft Visual Studio CoreCLR Debugger, ‘vsdbg.exe,’ renamed and configured to sideload a malicious DLL (vsdbg.dll). The installer deploys the Rapuncel infostealer as well as the Alinubx.sys kernel driver, which is used to kill antivirus software.
Source: bleepingcomputer.com