Apr. 10, 2018

Sodexo food services and facilities management company notified a number of customers that it was the victim of a targeted attack on its cinema vouchers platform Sodexo Filmology.
Source: securityaffairs.co
Apr. 10, 2018

Due to several bugs in the XVG code, you can exploit this feature by mining blocks with a spoofed timestamp. When you submit a mined block, as a malicious miner or pool, you simply set a false timestamp to this block one hour ago and XVG will then “think” the last block mined on that algorithm was one hour ago. Your next block, the subsequent block, will then have the correct time.
Apr. 10, 2018
Two new Matrix Ransomware variants were discovered this week by MalwareHunterTeamthat arebeing installed through hacked Remote Desktop services. While both of these variants encrypt your computer’s files, one is a bit more advanced with more debugging messages and the use of cipher to wipe free space.
Source: bleepingcomputer.com
Apr. 9, 2018

If you were mining for someone else, your earnings are considered wages, subject to regular wage withholding by your employer. If you were doing it as an independent contractor,those earnings have to be considered self-employment earnings. In other words, those earnings will not be reported as capital.
So you have both the initial difficulty of determining fair market value of the virtual currency and the added complication of properly categorizing your mining activity. Note, this is assuming employees or contractors are getting paid in cryptocurrency; regular salary paid in cash and similar payments are treated under standard income tax principles.
Apr. 9, 2018
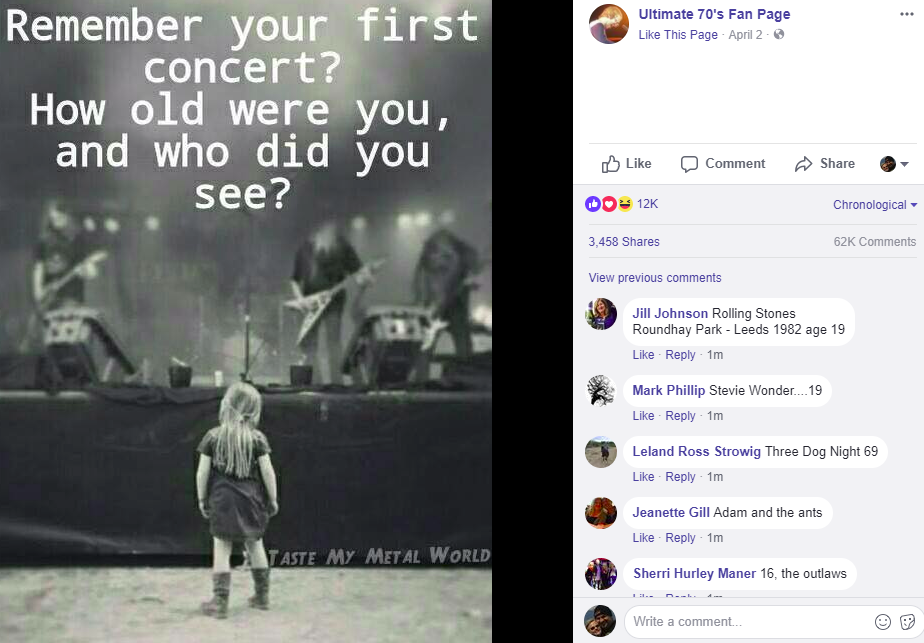
Social media sites are littered with seemingly innocuous little quizzes, games and surveys urging people to reminisce about specific topics, such as “What was your first job,” or “What was your first car?” The problem with participating in these informal surveys is that in doing so you may be inadvertently giving away the answers to “secret questions” that can be used to unlock access to a host of your online identities and accounts.
Apr. 9, 2018
Encrypting DNS traffic between your device and a ‘privacy-focused’ provider can keep someone from spying on where your browser is pointed or using DNS attacks to send you somewhere else.
Source: arstechnica.com
Apr. 9, 2018

The statement said the attack, which hit internet service providers and cut off web access for subscribers, was made possible by a vulnerability in routers from Cisco which had earlier issued a warning and provided a patch that some firms had failed to install over the Iranian new year holiday.
Source: reuters.com
Apr. 7, 2018
An Ohio court sentenced yesterday four high-ranking TERiX executives for their role in a pirating scheme through which they stole and resold Sun and Oracle firmware patches. Three of the four execs received prison sentences.
Source: bleepingcomputer.com
Apr. 7, 2018
Learn how to exploit Bluetooth Low Energy for IoT Devices using a step-by-step guide. In this post, we are using Gattacker to perform sniffing and replay based attacks.
Source: attify.com
Apr. 7, 2018
The company admitted on Twitter that it stores at least part of their customer’s passwords in plaintext. This is a big no-no in this day and age because if anyone breaches T-Mobile (and companies are breached all the time), they could likely guess or brute-force every user’s password. If the passwords were fully encrypted or hashed, it wouldn’t be that easy.
Apr. 7, 2018

Blockchain is not only crappy technology but a bad vision for the future. Its failure to achieve adoption to date is because systems built on trust, norms, and institutions inherently function better than the type of no-need-for-trusted-parties systems blockchain envisions. That’s permanent: no matter how much blockchain improves it is still headed in the wrong direction.
Source: medium.com
Apr. 7, 2018

Secure, affordable and convenient. That’s how the makers of the FUZE Card describe their creation, designed to act as a whole wallet in a single thin device. It can store up to 30 different credit cards and uses a lock to protect the data within.
Such a hit was it with consumers it raised nearly $2.5 million in Indiegogo funding, with the original cost starting at $160.
Apr. 7, 2018
I rarely think that the text I’m copying and pasting has something hidden within it that could reveal my sources. And I probably should worry about that because it’s incredibly easy to hide invisible characters—so-called “zero-width” characters—within text and use those as a watermark or fingerprint of sorts. In some situations, that could reveal to the original author who you are, or the fact that you copy pasted the original text and put it somewhere else.
Apr. 7, 2018
In 2016, the cyberinsurance market brought in around $3.5 billion in premiums globally, of which $3 billion came from US-based companies, according to the Organisation for Economic Co-operation and Development. That’s not an enormous amount of money compared to other insurance markets; motor vehicle insurance premiums in the US, for instance, total more than $200 billion annually. But cyberinsurance premiums have grown steadily at a rate of roughly 30 percent every year for the past five years, in an industry unaccustomed to such spikes.
Apr. 7, 2018

This is the third post in a series on implementing the Ethereum Virtual Machine in Clojure.
Source: nervous.io
Apr. 6, 2018
The Verge development team is preparing a hard-fork of the entire cryptocurrency code to fix the issue and revert the blockchain to a previous state before the attack to neutralize the hacker’s gains.
Source: bleepingcomputer.com
Apr. 6, 2018

Last week, on March 28, Delta was notified by [24]7.ai, a company that provides online chat services for Delta and many other companies, that [24]7.ai had been involved in a cyber incident. It is our understanding that the incident occurred at [24]7.ai from Sept. 26 to Oct. 12, 2017, and that during this time certain customer payment information for [24]7.ai clients, including Delta, may have been accessed – but no other customer personal information, such as passport, government ID, security or SkyMiles information was impacted.
Apr. 6, 2018
This week, two separate security alerts have revealed major holes in devices from Moxa, an industrial automation networking company. In one case, attackers could potentially send commands to a device’s operating system by using them as a username in a login attempt. In another, the private key for a Web server used to manage network devices could be retrieved through an HTTP GET request.
Apr. 6, 2018
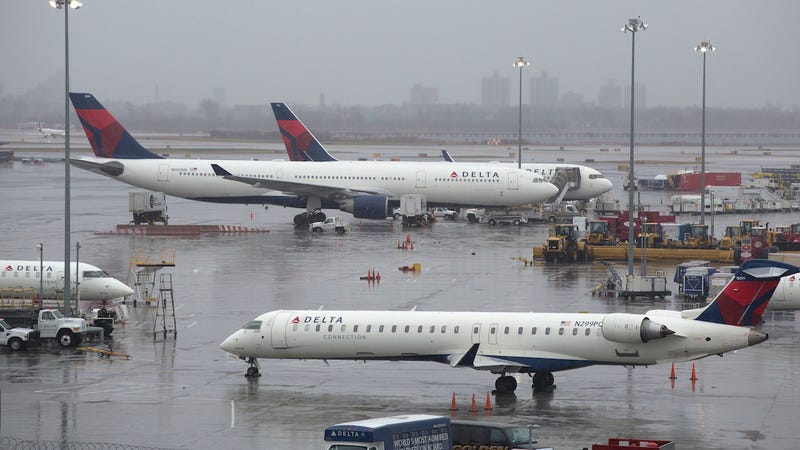
The nature of the malware involved has not been disclosed and it remains unclear whether the payment card information, which Delta say was entered by the customers themselves, got intercepted in transit or was improperly stored.
Source: gizmodo.com
Apr. 6, 2018

You can think of Chainalysis as a blockchain detective. The New York-based firm is best known for its forensic tools that help law enforcement agencies track the movement of bitcoin, but it also helps financial financial firms keep tabs on who is using digital currencies.
Source: fortune.com