Mar. 27, 2018
The Spectre attacks, published earlier this year, take advantage of the speculative execution features of modern processors to leak sensitive information. The new attack, named BranchScope by the researchers, shares some similarity with variant 2 of the Spectre attack, as both BranchScope and Spectre 2 take advantage of the behavior of the processor’s branch predictor.
Source: arstechnica.com
Mar. 27, 2018

We’re excited to announce our intention to support the Ethereum ERC20 technical standard for Coinbase in the coming months. This paves the way for supporting ERC20 assets across Coinbase products in the future, though we aren’t announcing support for any specific assets or features at this time. We are announcing this both internally and to the public as consistent with our process for adding new assets.
Mar. 26, 2018
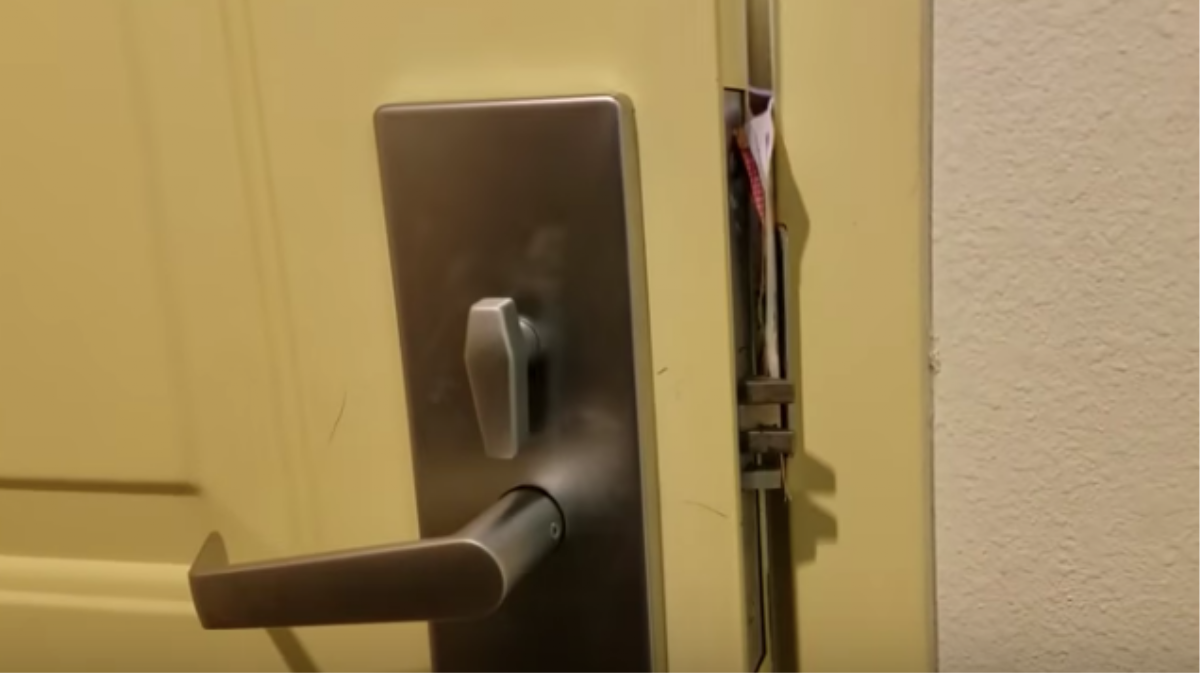
In a simple, yet sort of terrifying video, YouTuber and locksmith “MM Developer” demonstrates how easy it is to break into a hotel room door with just a paper restaurant menu—no social engineering or lock-picking skills required.
Source: vice.com
Mar. 26, 2018

Coming amidst a firestorm of scrutiny about how political operations can use and harvest consumer information, including from social media networks like Facebook, the UpGuard Cyber Risk Team can now reveal that a large code repository originating from AggregateIQ, a Canadian political data firm active in the 2016 US presidential race, was left publicly downloadable online. Revealed within this repository is a set of sophisticated applications, data management programs, advertising trackers, and information databases that collectively could be used to target and influence individuals through a variety of methods, including automated phone calls, emails, political websites, volunteer canvassing, and Facebook ads. Also exposed among these tools are numerous credentials, keys, hashes, usernames, and passwords to access other AIQ assets, including databases, social media accounts, and Amazon Web Services repositories, raising the possibility of attacks by any malicious actors encountering the exposure.
Mar. 26, 2018
Grey Heron was formed from other players in the government hacking space, including Hacking Team, a source familiar with the company said. In private conversations within the surveillance industry that were later detailed to Motherboard, Grey Heron has suggested it sees distancing itself from Hacking Team and its history as a benefit.
Source: vice.com
Mar. 26, 2018

According to Europol, the cybercriminals have been active since 2013, striking banks in over 40 countries in order to steal at least €1 billion, estimated at roughly €10 million per successful heist.
Source: zdnet.com
Mar. 26, 2018
Multiple security firms recently identified cryptocurrency mining service Coinhive as the top malicious threat to Web users, thanks to the tendency for Coinhive’s computer code to be used on hacked Web sites to steal the processing power of its visitors’ devices. This post looks at how Coinhive vaulted to the top of the threat list less than a year after its debut, and explores clues about the possible identities of the individuals behind the service.
Mar. 26, 2018
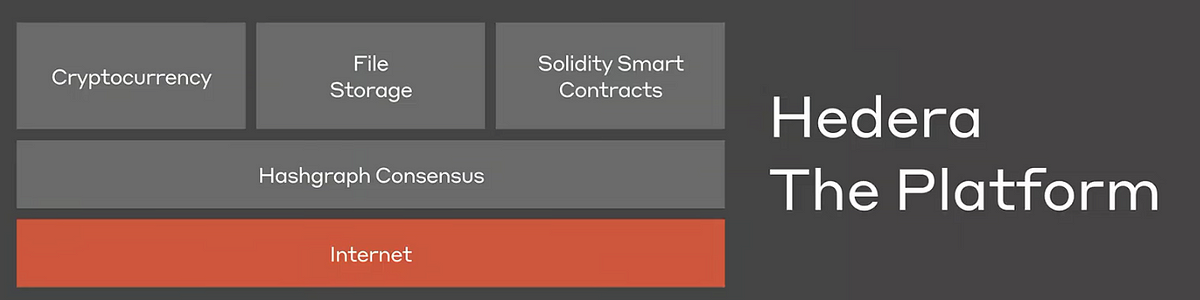
Two weeks ago, with more than 1,000 other Crypto enthusiasts, I had the pleasure of attending the NYC launch event for Hadera Hashgraph, a new public blockchain promising vastly faster throughput.
Source: medium.com
Mar. 26, 2018
There are many thought leaders trying to find alternatives to Proof of Work. The most promising one so far is Proof of Stake. There are already production-ready blockchains based on Proof of Stake like Nxt and Neo.
Ethereum is probably moving to Proof of Stake—their Casper project is already live on their test net.
Source: medium.com
Mar. 26, 2018
Virtual currency transactions are taxable by law just like transactions in any other property. The IRS has issued guidance in IRS Notice 2014-21for use by taxpayers and their return preparers that addresses transactions in virtual currency, also known as digital currency.
Source: irs.gov
Mar. 26, 2018

Trend Micro uncovered a new crypto mining campaign targeting Linux servers that exploit the CVE-2013-2618 flaw in Cacti’s Network Weathermap plug-in, which system administrators use to visualize network activity.
Source: securityaffairs.co
Mar. 25, 2018

According to the researcher Giovanni Collazo, querying the popularShodan search engine he found almost 2,300 servers exposed online that were runningetcd, which is a distributed key value store that provides a reliable way to store data across a cluster of machines.
Source: securityaffairs.co
Mar. 25, 2018
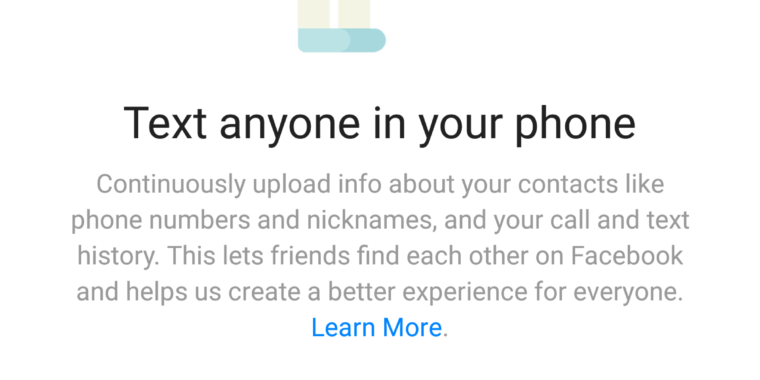
This past week, a New Zealand man was looking through the data Facebook had collected from him in an archive he had pulled down from the social networking site. While scanning the information Facebook had stored about his contacts, Dylan McKay discovered something distressing: Facebook also had about two years worth of phone call metadata from his Android phone, including names, phone numbers, and the length of each call made or received.
Mar. 25, 2018

This post describes a recent attack Minerva’s research team dissected, dubbed GhostMiner, after our solution prevented this infection at a customer site. It provides an example of how malicious miners are evolving to use advanced fileless techniques to succeed in mining Monero and spreading silently on a global scale. In this attack, we also witnessed how competing miners are fighting each other to generate more income for themselves, removing other miners on the endpoint.
Mar. 25, 2018
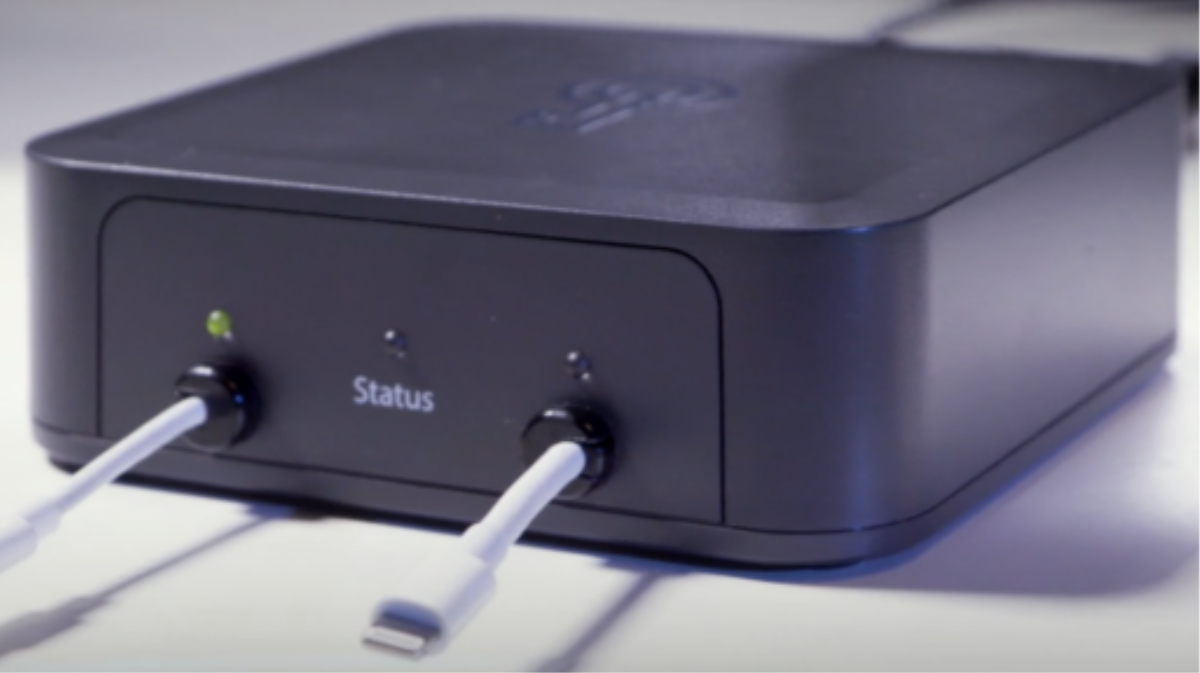
As the FBI pushes once again for backdoors in consumer encryption products, the State Department is apparently taking advantage of a $50 per iPhone unlocking product from Grayshift, a company with an ex-Apple engineer on its staff.
Source: vice.com
Mar. 25, 2018

The US military is working on an experimental laser technology that could create the sound of voices out of thin air by altering atoms. The US military’s Joint Non-Lethal Weapons Program, or JNLWD, thinks it can achieve this goal in the next few years.
Source: interestingengineering.com
Mar. 25, 2018

Two years ago, when we began taking on blockchain security engagements, there were no tools engineered for the work. No static analyzers, fuzzers, or reverse engineering tools for Ethereum.
Source: trailofbits.com
Mar. 25, 2018
Roy Jones says he got no training on how to handle issues that might inflame the Chinese government. “My job isn’t to decide whether Tibet is a country. I’m a customer care rep in Omaha, Nebraska,” he said.
Source: omaha.com
Mar. 25, 2018

In the wake of the Cambridge Analytica scandal, many Facebook users have been downloading their Facebook posts. And some of them are finding call and text-message logs from 2015 through 2017, although not the actual content of the calls or texts.
Source: tomsguide.com
Mar. 24, 2018

Over the past few months, I’ve been monitoring the proliferation of exploits for some of my disclosed WordPress Plugin and Joomla Extension vulnerabilities against Akamai customers. I started this observation process which leads to an expected conclusion – severe vulnerabilities like SQL Injection, RFI and LFI would receive the most attention for any CMS platform. While less severe vulnerabilities such as XSS and path disclosure would likely receive less attention from the attackers.