Sep. 16, 2026

In the mid-2010s, Chinese cyber espionage actors stole complementary data from a variety of sources that, together, would be useful for analyzing the U.S. intelligence apparatus. Various Chinese APT groups stole information from the health insurance company Anthem, credit reporting company Equifax, Marriott hotels, United Airlines, and, perhaps most significantly, security clearance information from the Office of Personnel Management.
Source: lawfaremedia.org
Sep. 15, 2026

ConnectWise has released urgent patches for a critical-severity vulnerability in the ScreenConnect remote access and support software that has been exploited in worm-like attacks. Tracked as CVE-2026-84869 (CVSS score of 9.9/10), the security defect is described as a missing authorization and improper privilege management issue. The bug creates “a condition in the ScreenConnect client that may allow files to be transferred and executed through an active remote session without authorization or Host confirmation in certain circumstances,” ConnectWise explains in its advisory.
Sep. 9, 2026

Businesses received a staggering amount of cyberattacks in June, according to Check Point, showing a rise of 20% over the previous 12 months. The breakout of AI agents from OpenAI in July to hack into the Hugging Face website, and subsequent similar events from Anthropic and Meta, indicate agentic-powered attacks will explode over the coming year. Currently, malicious hackers have the advantage because publicly released frontier models from the US incorporate guardrails that can’t distinguish between malicious or defensive activities. As a consequence, these models default to a refusal to get involved. Hugging Face discovered this the hard way when they attempted to utilize a model to defend against the OpenAI intrusion. Their solution was to adapt a Chinese open weight model to analyze the 17,000 attack logs, find the vulnerability, and contain the intrusion. With incidents like these happening more often, an arms race has begun with AI being both the problem and the solution.
Sep. 8, 2026

The Defense Innovation Unit (DIU), a development unit of the US Department of Defense, has tested a quantum sensor-based flight navigation system over the Pacific as part of the MagNav program. The DIU announced on Friday. This allows the position to be determined precisely without relying on GPS; for example, if it is jammed by the enemy in military conflicts, the GPS signal fails or cannot be received. The MagNav system, developed by Honeywell Aerospace, uses quantum sensors. These sensors detect changes in the Earth’s natural magnetic field and create a magnetic field map from the measurements. Based on this map, the system can determine the position in aircraft entirely independently of GPS signals, weather, and visibility conditions.
Sep. 8, 2026
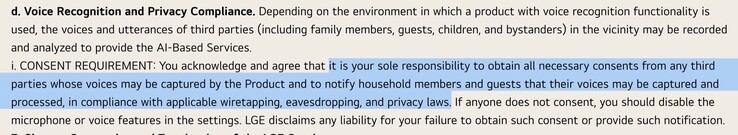
Anyone who owns an LG smart TV must inform all guests and family members that they are being monitored – this is required by LG’s current terms of use. Meanwhile, LG monitors install potential malware and surveillance software on a connected Windows computer.
Source: notebookcheck.net
Sep. 5, 2026

Using counterterrorism-grade surveillance against a prominent critic on a stretched legal theory makes federal charges against Swalwell unlikely by December 5, 2026, while inviting defense challenges to prosecutorial motive.
Source: icbrief.org
Sep. 4, 2026
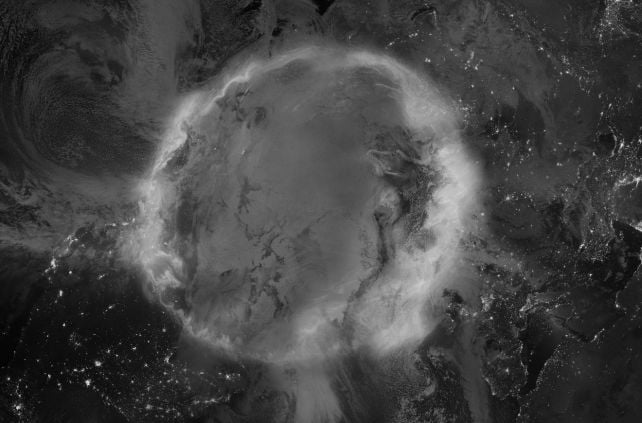
In November 2025, Earth was buffeted by several massive eruptions of solar material that slammed into the magnetosphere. GPS Glitched Across The US by as Much as 33 Feet. Scientists Have Never Seen This Before. Auroras seen from the International Space Station during the November 2025 solar superstorm. (Earth Science and Remote Sensing Unit, NASA Johnson Space Center)
Source: sciencealert.com
Aug. 30, 2026
 Photo by Raimond Klavins on Unsplash
Quantum infrastructure software firm Q-CTRL has completed itsfirst open-water field demonstration of a GPS-free, quantum-gravimetric maritime navigation system.
Source: gpsworld.com
Aug. 26, 2026

China’s hacking campaign targeted NASA, the Federal Reserve, the US Senate, the Justice Department, and more, according to the DOJ. For years, China’s military and intelligence agencies, which carry out hacking campaigns against targets around the globe, have grown increasingly reliant on a vast web of proxy devices that enable and obfuscate their targeting. Now the FBI has named and disrupted one key network of those proxies—and in doing so, revealed just how extensively the hackers who used it reached into American government institutions and US critical infrastructure.
Aug. 26, 2026
 Photo by Markus Winkler on Unsplash
Researchers affiliated with the University of Massachusetts Amherst have found that you can get payments out of certain expired contactless credit cards, a process detailed at the recent USENIX Security 2026 conference. Credit cards, the authors explain in their paper, have expiration dates, but the way these dates get checked and enforced isn’t consistent. Thus, they were able to devise an attack that makes expired contactless cards appear to be valid to payment terminals.
Aug. 23, 2026

Google’s Threat Intelligence Group tracked three separate suspected Russia-linked cyber espionage clusters. All three focus on the same thing: abusing authentication features that are supposed to protect accounts to access them instead. Threat actors target researchers, academics, government officials, think-tank analysts, and defense sector personnel across Europe and the United States. The three clusters are tracked as UNC6293, UNC7005, and UNC5976, and while they operate differently and with different tools, Google published them together for a reason.
Aug. 23, 2026
 Photo by Pawel Czerwinski on Unsplash
Shortly after loading the AliExpress homepage, audio from my phone would stop playing. Closing the AliExpress tab fixes it immediately. Muting the tab/Firefox/Windows does not help, and there is no visible video, music, or other media playing on the page.
Source: blog.laserphile.com
Aug. 23, 2026
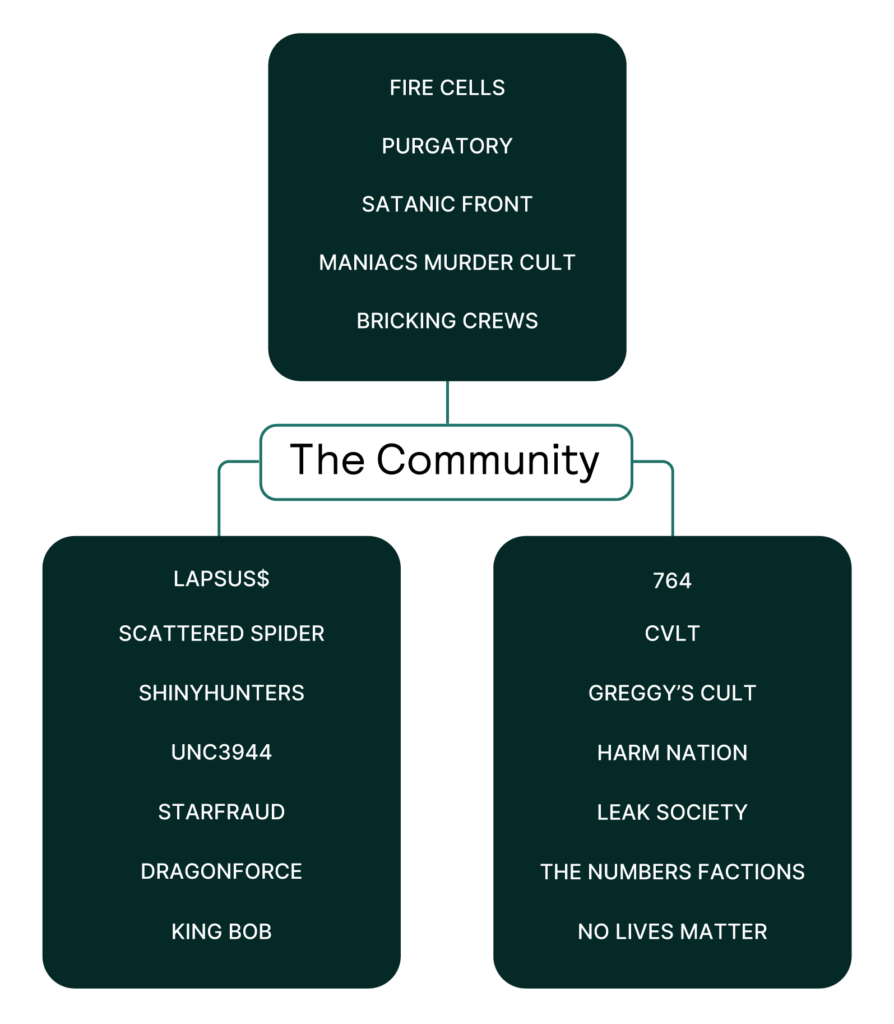
We dive into the decentralized architecture of “The Com,” exposing its hybrid ecosystem of hacking, extortion, and real-life violence. The Community, more widely known as “The Com” is a sophisticated hybrid threat ecosystem in which cybercrime serves as the venture capital for domestic terrorism. Existing since the early 2010s, it operates in the “edgesphere”, a grey area where mainstream social media overlaps with underground criminal networks, blending nihilistic violent extremism (NVE) with high-level financial fraud. In The Com, cybercrime against Fortune 500 companies is the primary revenue stream used by members to fund a domestic terror network that aims to radicalize youth and encourage real-world violence.
Aug. 23, 2026
 Photo by Boitumelo on Unsplash
An estimated 4 340 URLs related to nihilistic violent extremism were referred during the initiative organised by Europol’s EU Internet Referral Unit - EU IRU and the Spanish Intelligence Centre against Terrorism and Organised Crime (CITCO). This successful action complements the efforts undertaken within Project COMPASS, coordinated by Europol’s European Counter Terrorism Centre, which unites law enforcement authorities from EU…
Source: europol.europa.eu
Aug. 23, 2026

The FBI is warning the public about Hacker Com, one of three subsets of the growing and evolving online threat group known as The Com, short for The Community, a primarily English speaking, international, online ecosystem comprised of multiple interconnected networks whose members, many of whom are minors, engage in a variety of criminal violations.
Source: fbi.gov
Aug. 21, 2026
Cybersecurity researchers from TU Graz have disclosed a highly sophisticated Remote-Timer-as-a-Service side-channel execution flaw against serverless edge environments. In a controlled production test, this cloudflare workers spectre attack (a modern evolution of the foundational CVE-2017-5753 Spectre flaw) successfully leaked a JSON Web Token (JWT) from a co-located Worker at an astonishing rate of 12 bits per second (at 99.16% accuracy)—nearly 360 times faster than similar attacks demonstrated in 2021.
Aug. 21, 2026
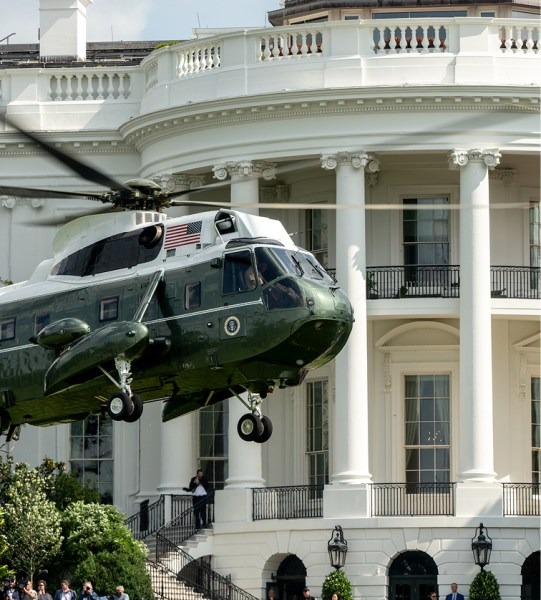
The Memorandum directs agencies to incentivize co-development of space transportation infrastructure with private sector partners, expedite permitting and environmental reviews, develop fair and transparent cost recovery policies for common space services and infrastructure, and develop range scheduling criteria and publish range schedules to maximize allocation of launch resources.
Source: whitehouse.gov
Aug. 20, 2026
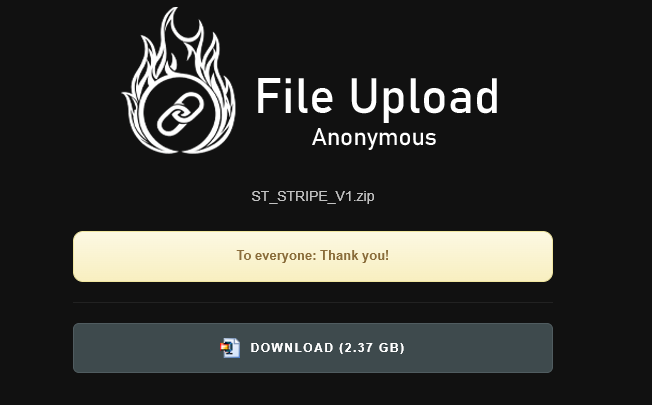
On August 18th, 2026, a data release occurred on the illicit forum pwnforums. The threat actor known as Satanic published sensitive information extracted from hundreds of vendors utilizing the Stripe payment platform. Figure 1: The initial forum post by Satanic announcing the breach, detailing the compromise of databases and 1,033 API keys, totaling 33GB, along with millions of email matches. Satanic is a known entity within the cybercrime ecosystem, previously verified by Hudson Rock researchers for their involvement in large-scale breaches. We previously documented their activities in the Hot Topic breach. Satanic is a known entity within the cybercrime ecosystem, previously verified by Hudson Rock researchers for their involvement in large-scale breaches. We previously documented their activities in the Hot Topic breach.
Aug. 12, 2026
 Photo by Luca Cavallin on Unsplash
Security researchers found that in less than 60 seconds, they could open a hatch on a plane’s exterior, plug in a tiny device, and redirect the aircraft’s autopilot or sabotage its flight plan. Even as the digital components of so many life-critical systems have proven susceptible to cybersabotage—cars, medical devices, even water utilities and power grids—the computer systems of airplanes have, thankfully, remained uniquely inaccessible to hackers. But one group of academic researchers has spent years testing a different, devious approach to aviation cybersecurity. Perhaps, they suggest, a plane could be hacked the same way that spies and saboteurs have targeted other high-value, offline computers: by surreptitiously gaining physical access to one and plugging in a device designed to silently run the attackers’ malicious code.
Aug. 10, 2026
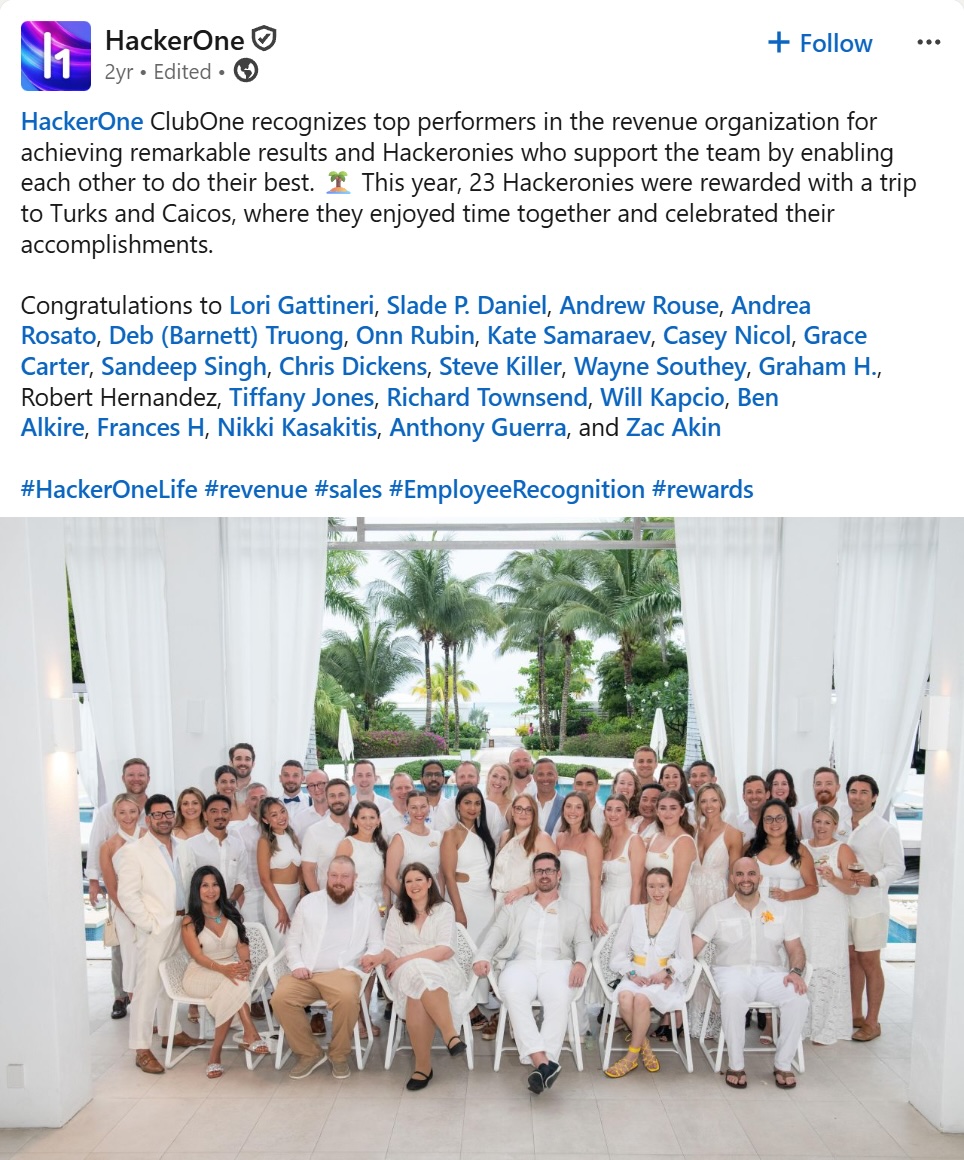
So…what’s going on at HackerOne lately? It might be time for a wellness check. If you are new to the bug bounty space (1-3 years), you might not have any idea what I’m talking about. But as a properly washed-up bug bounty hunter who lived through the golden era of HackerOne, I think it’s time to address the elephant in the room. For some context, I started as a hacker on HackerOne in 2017. When I began working in tech, that hands-on experience was extremely useful for managing a bug bounty program, since I knew what researchers wanted, and how to interact with them.