Jun. 12, 2018
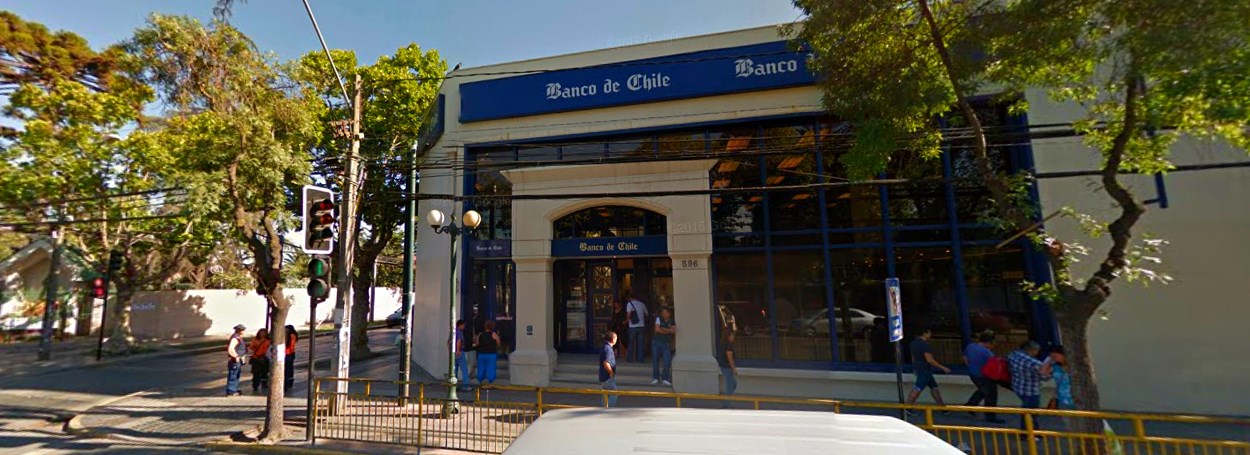
Hackers have used a disk-wiping malware to sabotage hundreds of computers at a bank in Chile to distract staff while they were attempting to steal money via the bank’s SWIFT money transferring system. The attempted hack took place on May 24, this year. On that day, the Banco de Chile, the country’s biggest bank, reported all-around systems failures that affected the computers at several of its branches.
Jun. 9, 2018
China’s state hackers have reportedly stolen a large amount of highly-sensitive US navy data on its undersea warfare, including plans for supersonic anti-ship missiles on submarines. Government experts were said to have compromised the computers of a US navy contractor, giving them access to the information, according to the Washington Post, citing unnamed American officials. They said – on the condition of anonymity about an ongoing investigation – that the security breaches were believed to have taken place in January and February.
Jun. 8, 2018

Adobe is aware of a report that an exploit for CVE-2018-5002 exists in the wild, and is being used in limited, targeted attacks against Windows users. These attacks leverage Office documents with embedded malicious FlashPlayercontent distributed via email. Unlike the critical vulnerabilities patched in Adobe’sMarch, Apriland May updates, CVE-2018-5002 isn’t a remotely exploitable flaw that cybercriminals might decide to exploit in future, it’s one that we only know about because they’re exploiting it now, a so-called zero-day.
Jun. 6, 2018

If Artificial Intelligence (AI) is increasingly able to recognise and classify faces, then perhaps the only way to counter this creeping surveillance is to use another AI to defeat it. We’re in the early years of AI-powered image and face recognition but already researchers at the University of Toronto have come up with a way that this might be possible. The principal at the heart of this technique is adversarial training, in which a neural AI network’s image recognition is disrupted by a second trained to understand how it works.
Jun. 6, 2018
Malta, an island nation in the Mediterranean Sea, is completing the first ever attempt by a nation state to tie citizen records to the blockchain. If successful, a scaled-up version of the pilot program will give Malta’s 400,000 residents the ability to retrieve and share educational records and transcripts for free. What’s more, it wouldprovide a proof-of-concept that could inspire other countries to adopt similar programs.
Jun. 6, 2018
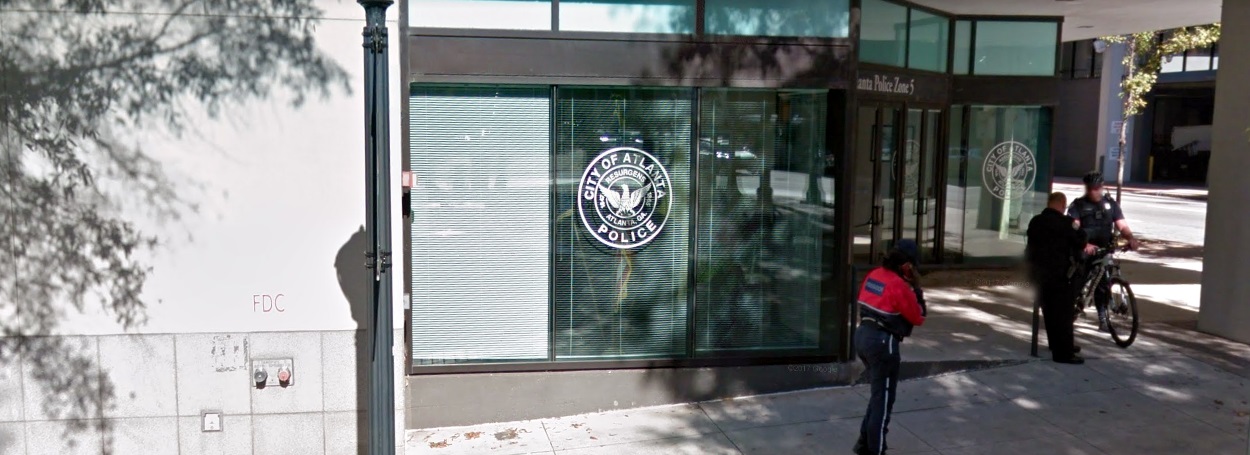
The Atlanta Police Department has lost years worth of police car dashcam videos following the March ransomware attack that affected most of the city’s IT infrastructure. Chief Shields said footage from body-worn cameras was not compromised in the cyber-attack that crippled Atlanta city IT systems for almost two months, but only videos recorded by police car dashcams. The normal train of thought is that the loss of the dashcam data could affect some DUI investigations, but Chief Shields downplayed the importance of the dashcam footage in pursuing DUI charges.
Jun. 6, 2018
Family genealogy and DNA testing site MyHeritage announced on Monday a security breach during which an attacker made off with account details for over 92 million MyHeritage users. The incident came to light after a security researcher found an archive on a third-party server containing the personal details of 92,283,889 MyHeritage users. The archive contained only emails and hashed passwords, but not payment card details or DNA test results.
Jun. 2, 2018

A popular fitness app that claims over six million users was leaking private and sensitive data, including health information and private messages sent between users. PumpUp, an Ontario-based company, bills itself as a fitness community, allowing subscribers to discover new workouts and record their results, and get advice from fitness coaches and other users. But the company left a core backend server, hosted on Amazon’s cloud, exposed without a password, allowing anyone to see who was signing on and who was sending messages — and their contents — in real-time.
Jun. 2, 2018
A hacker briefly took over Ticketfly’s website, defacing it with a picture of the V for Vendetta character and a claim of responsibility. The hacker also sent Motherboard files of what they say is employee and customer information taken from Ticketfly’s database. Ticketfly, which is owned by Eventbrite, took down the site and posted a message saying that the company had been “the target of a cyber incident.”
Jun. 2, 2018
The vulnerability has been present and exploitable in Steam for at least 10 years, according to Tom Court, a security researcher at Contextis, who wrote about the bug on Wednesday. Court said the bug left all 125 million Steam users vulnerable until March of this year, when Valve, the developers of Steam, patched it. In other words, by exploiting this bug, hackers could have executed code on the victim’s machine, effectively taking full control over it.
May. 31, 2018
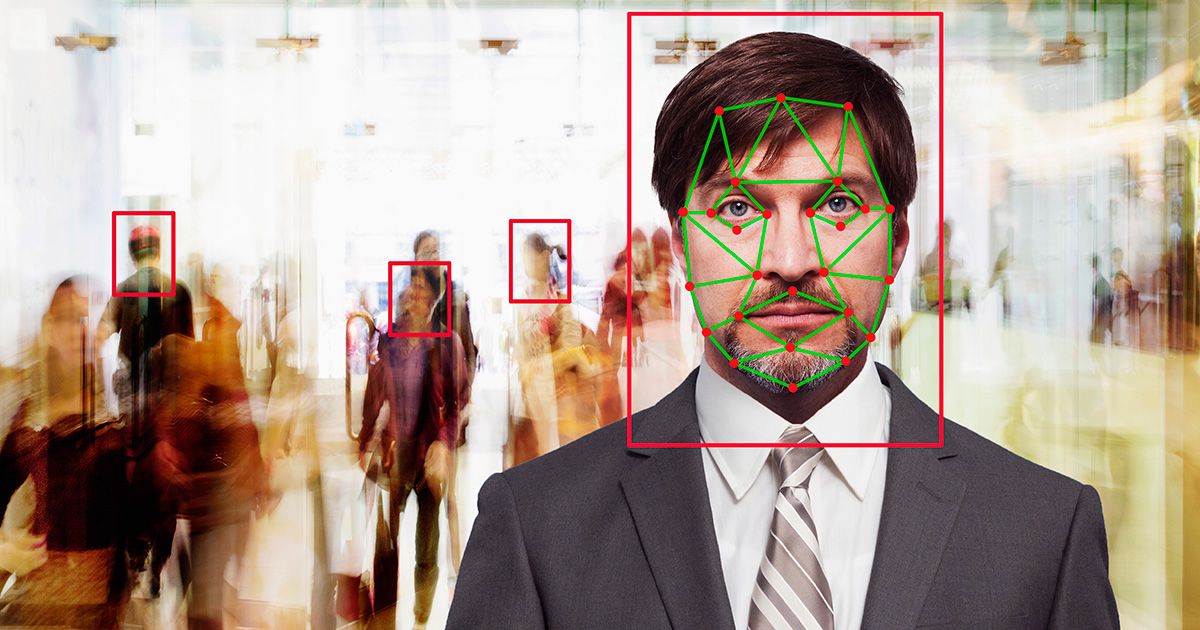
In its letter, the ACLU argues that Amazon, which has in the past opposed secret government surveillance, should not be in the business of selling AFR technology that the company claims can “identify people in real-time by instantaneously searching databases containing tens of millions of faces.” Further, the ACLU insists, Rekognition’s capability to track “persons of interest,” coupled with its other features which “read like a user manual for authoritarian surveillance,” lends itself to the violation and abuse of individuals’ civil rights. Amazon naturally disagrees.
May. 30, 2018
Using sonic and ultrasonic soundwaves as a weapon, researchers can disrupt the read, write and storage functions of a hard disk drive (HDD). The method can also be used to crash the host operating system, and in some cases damage targeted drives. Researchers said the attack can be performed by “nearby emitters” that target a computer’s HDD; so, the attacks could be performed by an adversary using inexpensive off-the-shelf speakers or could also be carried out via laptop or desktop speakers.
May. 30, 2018

The Git community has disclosed an industry-wide security vulnerability in Git that can lead to arbitrary code execution when a user operates in a malicious repository. This vulnerability has been assigned CVE 2018-11235 by Mitre, the organization that assigns unique numbers to track security vulnerabilities in software. Git 2.17.1 and Git for Windows 2.17.1 (2) were released today and include this fix.
May. 30, 2018

According to reporting of trusted third parties, HIDDEN COBRA actors have likely been using both Joanap and Brambul malware since at least 2009 to target multiple victims globally and in the United States—including the media, aerospace, financial, and critical infrastructure sectors. According to reporting of trusted third parties, HIDDEN COBRA actors have likely been using both Joanap and Brambul malware since at least 2009 to target multiple victims globally and in the United States—including the media, aerospace, financial, and critical infrastructure sectors. Users and administrators should review the information related to Joanap and Brambul from the Operation Blockbuster Destructive Malware Report [1] in conjunction with the IP addresses listed in the .csv
May. 30, 2018
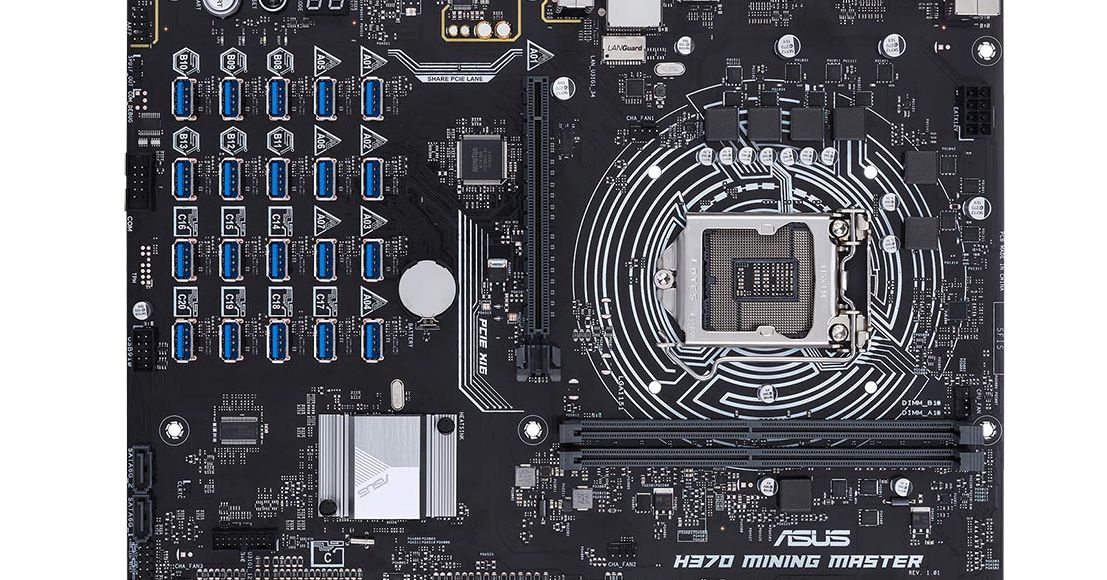
Asus announced the H370 Mining Master motherboard, which is specifically designed for cryptocurrency mining. It supports up to 20 graphics cards along with streamlined connectivity by allowing USB riser cables to plug directly into the PCB over PCIe. Asus announced the H370 Mining Master motherboard today, which is specifically designed for cryptocurrency mining.
It supports up to 20 graphics cards — yes, 20 — along with streamlined connectivity by allowing USB riser cables to plug directly into the PCB over PCIe. Asus’ approach here is going to make maintenance easier, ensure fewer PCIe disconnects, and more accurate diagnostics. This is a better format than just plugging in graphics cards to the motherboard via PCIe, like you would in a gaming desktop, the company says.
May. 29, 2018
Security researchers have discovered a series of new vulnerabilities in EOS blockchain platform, one of which could allow remote hackers to take complete control over the node servers running the critical blockchain-based applications. EOS is an open source smart contract platform, known as ‘Blockchain 3.0,’ that allows developers to build decentralized applications over blockchain infrastructure, just like Ethereum. Discovered by Chinese security researchers at Qihoo 360—Yuki Chen of Vulcan team and Zhiniang Peng of Core security team—the vulnerability is a buffer out-of-bounds write issue which resides in the function used by nodes server to parse contracts.
May. 29, 2018
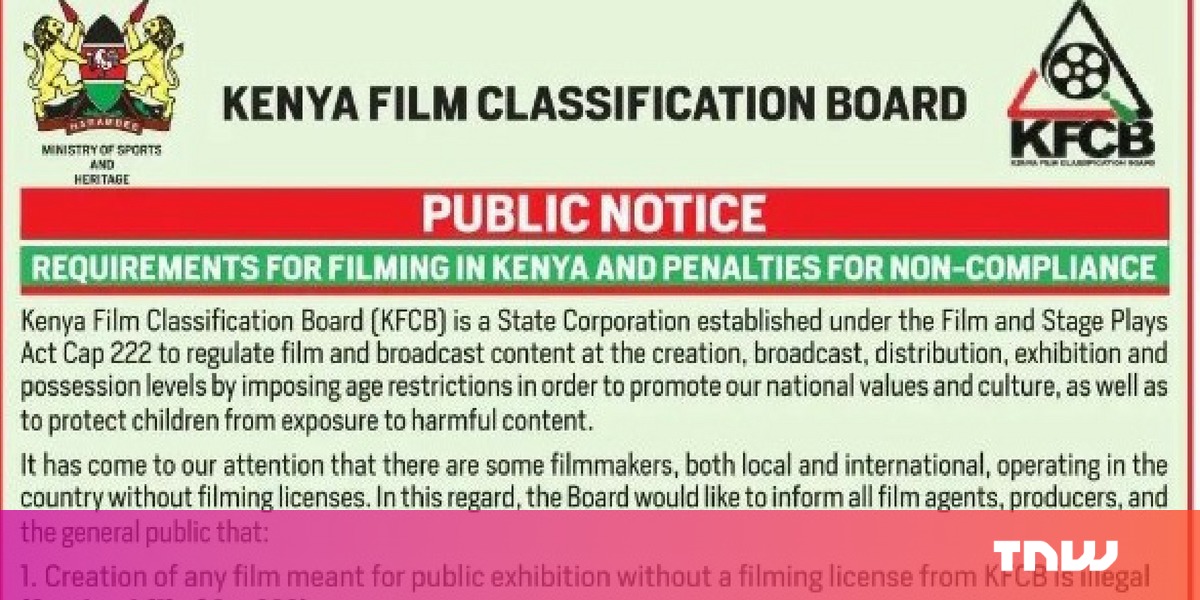
A new law is set to come into effect from May 28th, 2018 inKenyaregarding the publishing and broadcasting of any videos for public consumption. Specifically, theKenya Film and Classification Board(KFCB) states that, according to the law, anyone in Kenya broadcasting any videos for public viewing (including on social media and the Internet) will be required to have a filming license. Those who fail to register for a filming license with the KFCB face imprisonment or a fine.
May. 29, 2018

Two Canadian banks warned Monday they have been targeted by hackers, and that the personal information of tens of thousands of customers may have been stolen — something that appeared to be confirmed in a letter to the media from someone who said they were demanding a $1-million ransom from the banks. CIBC-ownedSimplii Financial was the first to warn on Monday morningthat hackers had accessed thepersonal and account information of more than 40,000 of the bank’s customers. The bank said it received a tip over the weekend that hackers had obtained the data, and after a preliminary investigation decided to go public on Monday.
May. 28, 2018
Cryptocurrency trading app Taylorsuffered a catastrophic hack on May 22 that resulted in the loss of over 2,500 ETH, valued at $1.5 million. In addition, the trading platform lost 7% of the total TAY token supply, potentially crippling the development of the trading software. According to the official statement, the only tokens that remain in the Taylor fund are those in the Founders’ and Advisors’ pools that are held in aninaccessible vesting contract.
May. 28, 2018

A man watched helplessly as cybercriminals stole £9,000 (nearly US$12,000) from his account at British bank TSB while he waited – for four-and-a-half hours – to get through to the bank’s fraud line, according to a BBC report. Ben Alford, of Weymouth in the United Kingdom, has described how he put in a call to TSB after noticing that somebody had taken out a loan in his name from another bank. While he was logged into his TSB online account and waited for the bank’s fraud department to deal with his phone call, he saw how two sums – £5,000 and £4,000 – were stolen from his account in two transactions.