May. 24, 2018

Federal prosecutors have charged three men with carrying out a deadly hoax known as “swatting,” in which perpetrators call or message a target’s local 911 operators claiming a fake hostage situation or a bomb threat in progress at the target’s address — with the expectation that local police may respond to the scene with deadly force. While only one of the three men is accused of making the phony call to police that got an innocent man shot and killed, investigators say the other two men’s efforts to taunt and deceive one another ultimately helped point the gun. According to prosecutors,the tragic hoax started with a dispute over a match in the online game “Call of Duty.”
May. 24, 2018
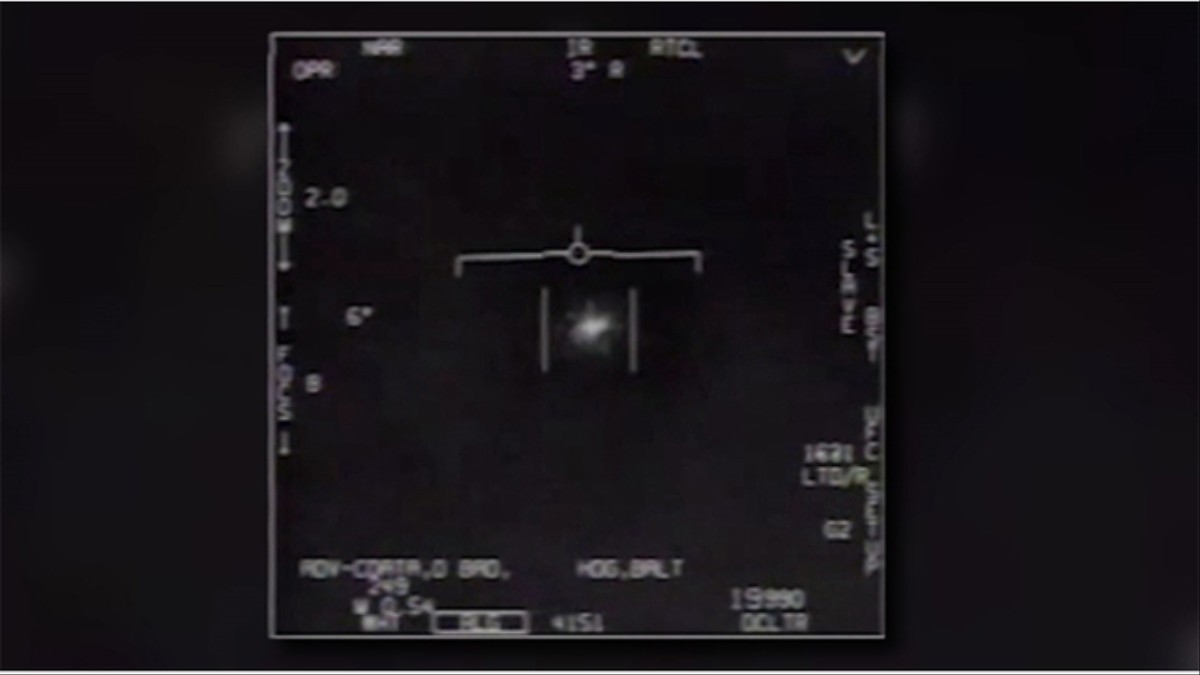
Now, a local investigative news team in Las Vegas obtained a 13-page document prepared for the military that analyzes what happened that day in 2004. The investigation was led by George Knapp, a journalist who made a name for himself in the 80s for substantiating parts of a story peddled by the prominent UFOlogist Bob Lazar, who claimed to have worked at Area 51. The report describes how the Anomalous Aerial Vehicle (AAV) seen by the two F18 pilots were able to “descend ‘very rapidly’ from approximately 60,000 feet down to approximately 50 feet in a matter of seconds.”
May. 24, 2018
A Portland family contacted Amazon to investigate after they say a private conversation in their home was recorded by Amazon’s Alexa — the voice-controlled smart speaker — and that the recorded audio was sent to the phone of a random person in Seattle, who was in the family’s contact list. A Portland family contacted Amazon to investigate after they say a private conversation in their home was recorded by Amazon’s Alexa — the voice-controlled smart speaker — and that the recorded audio was sent to the phone of a random person in Seattle, who was in the family’s contact list.
May. 24, 2018

A new report by the FBI’s Internet Crime Complaint Center has shown that complaints about scams and fraud are rising now at a record high and have resulted in reported losses of up to $1.42 billion In a typical BEC scam, a criminal dupes a company’s finance department into carrying out an unauthorized transfer of funds. Importantly, the target must be fooled into believing that the request has come from an executive within the company or from an outside firm that does business with it, so the scam involves a measure of social engineering, email spoofing, or computer intrusion.
May. 24, 2018
A malicious miner successfully executed a double spend attack on the Bitcoin Gold network last week, making BTG at least the third altcoin to succumb to a network attack during that timespan. Bitcoin Gold director of communications Edward Iskra first warned users about the attack on May 18, explaining that a malicious miner was using the exploit to steal funds from cryptocurrency exchanges. To execute the attack, the miner acquired at least 51 percent of the network’s total hashpower, which provided them with temporary control of the blockchain.
May. 23, 2018
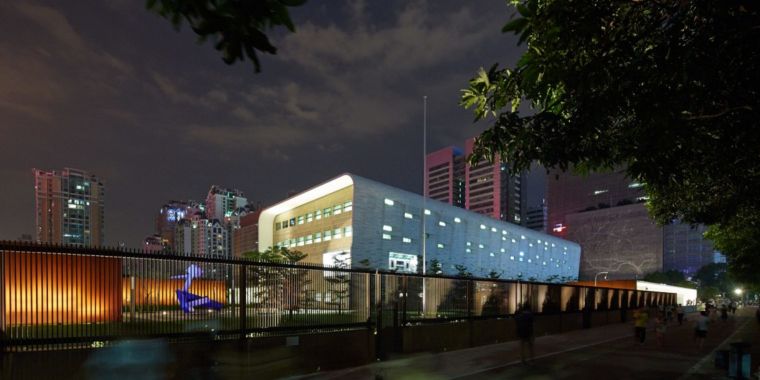
The case draws eerie similarities to mysterious ‘health attacks’ in Cuba. The US government issued an alert Wednesday following reports that a government employee stationed in southern China experienced “subtle and vague, but abnormal, sensations of sound and pressure” and sustained a brain injury.
Responding to an email from the New York Times, a spokesperson for the United States Embassy in Beijing said that the unnamed employee was working in the US consulate in the city of Guangzhou, just northwest of Hong Kong, and experienced a variety of symptoms from late 2017 until April of this year. In statements to the BBC, she noted that the employee had been sent back to the US. Last Friday, the 18th of May, “the embassy was told that the clinical findings of [an] evaluation matched mild traumatic brain injury,” she wrote.
May. 23, 2018
Discovered by Kaspersky Lab researchers, this backdoor grants an attacker access to the device’s web panel, and there’s no way in which device owners can disable this secret account. To prevent abuse, Kaspersky researchers have refrained from disclosing the backdoor’s account username and password. The backdoor account (CVE-2018-6213) is just one of four vulnerabilities Kaspersky researchers found in the firmware of these devices following a recent security audit.
May. 23, 2018
For several months, Talos has been working with public- and private-sector threat intelligence partners and law enforcement in researching an advanced, likely state-sponsored or state-affiliated actor’s widespread use of a sophisticated modular malware system we call ‘VPNFilter.’ We have not completed our research, but recent events have convinced us that the correct way forward is to now share our findings so that affected parties can take the appropriate action to defend themselves. In particular, the code of this malware overlaps with versions of the BlackEnergy malware — which was responsible for multiple large-scale attacks that targeted devices in Ukraine.
May. 23, 2018

After 13 months of research, the team discovered 14 vulnerabilities which could place connected cars at risk of compromise. The tests were conducted with BMW’s backing and in laboratory conditions. Impacted vehicles are included in the automaker’s i Series, X1 sDrive, 5 Series, and 7 Series.
In total, as documented in Keen Security Lab’s technical report (.PDF), nine of the attack scenarios presented required physical access to the target vehicle, while five were based on using a mobile Internet connection. The vulnerabilities permitted attackers to access the head unit — otherwise known as the infotainment system — and T-box components including the Telematics Control Unit and Central Gateway Module of the vehicles involved in the tests, leading to the creation and deployment of exploit chains designed to seize control of CAN buses. The exposure of CAN buses to attack is a serious issue considering that these buses connect all of a car’s functions.
May. 23, 2018
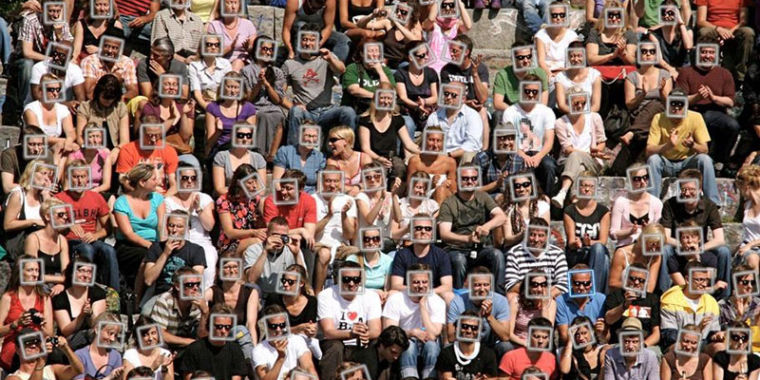
Amazon is actively courting law-enforcement agencies to use a cloud-based facial-recognition service that can identify people in real time, the American Civil Liberties Union reported Tuesday, citing the documents obtained from two US departments. The service, which Amazon markets under the name Rekognition, can recognize as many as 100 people in a single image and can compare images against databases containing tens of millions of faces. Company executives describe deployment by law enforcement agencies as common use case.
May. 22, 2018
A security hole in a Comcast service-activation website allowed anyone to obtain a customer’s Wi-Fi network name and password by entering the customer’s account number and a partial street address, ZDNet reported yesterday. The problem would have let attackers ‘rename Wi-Fi network names and passwords, temporarily locking users out’ of their home networks, ZDNet wrote. Obviously, an attacker could also use a Wi-Fi network name and password to log into an unsuspecting Comcast customer’s home network.
May. 22, 2018
Cryptocurrency enthusiasts are keen on telling ordinary civilians how safe and secure the Blockchain protocols powering their favorite coins are. Indeed, major cryptocurrencies like Bitcoin and Ethereum have maintained their security quite well—better, arguably, than any other digital asset/payment system in history—which is pretty remarkable, considering that they are unbacked digital money free from any single party’s control with an effective multi-billion dollar bounty on their proverbial heads. Last month, an as-of-yet unidentified attacker was able to severally compromise Verge, a relatively small, privacy-focused cryptocurrency.
May. 22, 2018
SleuthQL aims to augment an assessor’s ability to discover SQL injection points by automating some of the request analysis required during a web application assessment. SleuthQL is a Python 3 script to search Burp Suite’s request history for parameters and values that match syntax matching that of database languages, such as SQL. It judges a parameter or value based on whether it matches a regular expression associated with database queries.
May. 22, 2018
Both Google and Microsoft researchers discovered the bug independently. The bugs work similarly to the Meltdown and Spectre bugs, a reason why they were classified as ‘variant 3a’ and ‘variant 4’ instead of separate vulnerabilities altogether. Variant 3a is a variation of the Meltdown flaw, while Variant 4 is a new Spectre-like attack.
The most important of these two is Variant 4. Both bugs occur for the same reason —speculative execution— a feature found in all modern CPUs that has the role of improving performance by computing operations in advance and later discarding unneeded data. The difference is that Variant 4 affects a different part of the speculative execution process —the data inside the ‘store buffer’ inside a CPU’s cache.
May. 22, 2018
“Now we have a big contract with Vodafone, and every month Vodafone has to give machine readable data to city hall. Before, that didn’t happen. They just took all the data and used it for their own benefit”
In 2015 Ada Colau, an activist with no experience in government, became mayor of Barcelona. She called for a democratic revolution, and for the last two years city hall, working with civic-minded coders and cryptographers, has been designing the technological tools to make it happen. Their efforts have centred on two things.
May. 22, 2018

The mobile app, TeenSafe, bills itself as a ‘secure’ monitoring app for iOS and Android, which lets parents view their child’s text messages and location, monitor who they’re calling and when, access their web browsing history, and find out which apps they have installed. Although teen monitoring apps are controversial and privacy-invasive, the company says it doesn’t require parents to obtain the consent of their children. But the Los Angeles, Calif.-based company left its servers, hosted on Amazon’s cloud, unprotected and accessible by anyone without a password.
May. 21, 2018

In November 2017, a pseudonymous actor exploited a vulnerability in Parity’s multi-signature Ethereum wallet library that rendered half a million ether inaccessible to their owners. Ironically, the culprit, Devops199, was trying to patch another vulnerability that allowed hackers to steal $32 million from Parity’s multi-signature wallet accounts back in July of 2017. While tinkering with the popular service’s smart contracts, Devops199 blundered his way into complete ownership of the library that houses the entirety of Parity’s multi-signature wallet accounts.
May. 21, 2018

We, as malware analysts, are always in need of new samples to analyze in order to learn, train or develop new techniques and defenses. One of the most common questions I get is “Where to find malware to analyze?” so I’m sharing here my private collection of repositories, databases and lists which I use onadaily basis.
Some of them are updated frequentlyandsome of them are not. The short description under each link wasn’t written by me, it was written by the owners of the repositories.
May. 21, 2018

The News4 I-Team found dozens of the potential spy devices while driving around Washington, D.C., Maryland and Northern Virginia. The technology can be as small as a suitcase, placed anywhere at any time, and it’s used to track cell phones and intercept calls. The News4 I-Team found dozens of potential spy devices while driving around Washington, D.C., Maryland and Northern Virginia.
May. 21, 2018
T-Mobile is investigating a retail store employee who allegedly made unauthorized changes to a subscriber’s account in an elaborate scheme to steal the customer’s three-letter Instagram username. The modifications, which could have let the rogue employee empty bank accounts associated with the targeted T-Mobile subscriber, were made even though the victim customer already had taken steps recommended by the mobile carrier to help minimize the risks of account takeover. So-called “port out” scams allow crooks to intercept your calls and messages while your phone goes dark.