Apr. 19, 2018

Researchers found a new iOS vulnerability called ‘trustjacking,’ which exploits a feature called iTunes Wi-Fi Sync to give attackers persistent control over victims’ devices.
Source: threatpost.com
Apr. 19, 2018

An arbitrary file write vulnerability is where a user can create or modify a file in a location they could not normally access. This might be due to a privileged service incorrectly sanitizing information passed by the user or due to a symbolic link planting attack where the user can write a link into a location which is subsequently used by the privileged service. The ideal vulnerability is one where the attacking user not only controls the location of the file being written but also the entire contents.
Apr. 19, 2018
The patent, which was filed in 2014 but approved on Tuesday, comes at a time when regulators’ desire to track and police cryptocurrency is running up against the technology’s core promises of pseudonymity for users. Bitcoin users, for example, are represented in the virtual currencies ledger by strings of text and numbers generated by a cryptographic algorithm. Taxation for Bitcoin thus relies on self-reporting.
Apr. 19, 2018

Ethereum contracts are immutable but there is a way to design contracts which can be upgraded, so you can fix bugs quickly and add features. We’ll see how to create upgradable contracts.
Source: zohaib.me
Apr. 19, 2018
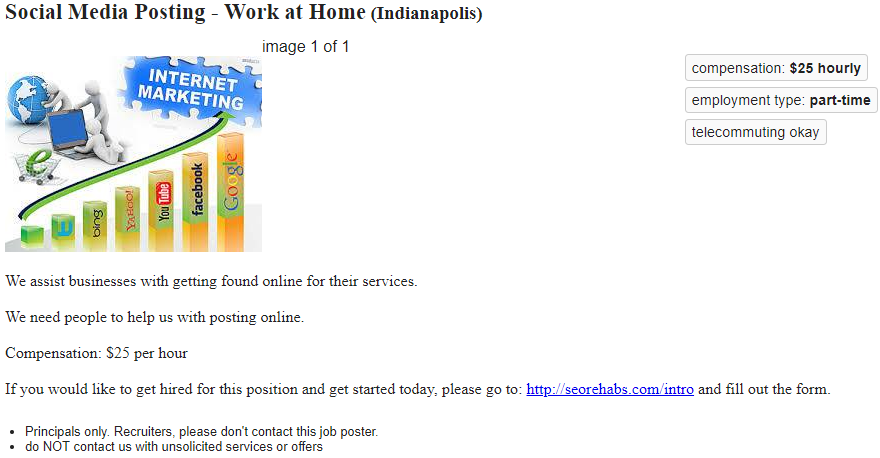
Bryan Seely, a security expert who has written extensively about the use of fake search listings to conduct online bait-and-switch scams, said the purpose of sites like those that Seorehabs pays people to create is to funnel calls to a handful of switchboards that then sell the leads to rehab centers that have agreed to pay for them. Many rehab facilities will pay hundreds of dollars for leads that may ultimately lead to a new patient. After all, Seely said, some facilities can then turn around and bill insurance providers for thousands of dollars per patient.
Apr. 19, 2018
The malware was designed to copy the credentials in a way that wouldn’t be detected by antivirus programs. The copying process, for instance, remained active for less than one minute. The malware didn’t steal general credentials, and it copied cookies and saved passwords by querying copies of the original cookies and LoginData files rather than through other means.
Source: arstechnica.com
Apr. 19, 2018
UPDATE, 4/18/18 – it appears Basecoin has changed its name to “Basis Protocol” and has alsoraised $133 million from top Valley investors anyway. Despite the fact that it’s an economic dumpster fire.
Source: prestonbyrne.com
Apr. 19, 2018
Former Apple security engineer Braden Thomas, who now works for a company called Grayshift, warned customers who had bought his GrayKey iPhone unlocking tool that iOS 11.3 would make it a bit harder for cops to get evidence and data out of seized iPhones. A change in the beta didn’t break GrayKey, but would require cops to use GrayKey on phones within a week of them being last unlocked.
Apr. 19, 2018

Recently, we came across a Python-based sample dropped by an exploit kit. Although it arrives under the disguise of a MinerBlocker, it has nothing in common with miners. In fact, it seems to be PBot/PythonBot: a Python-based adware.
Source: malwarebytes.com
Apr. 19, 2018
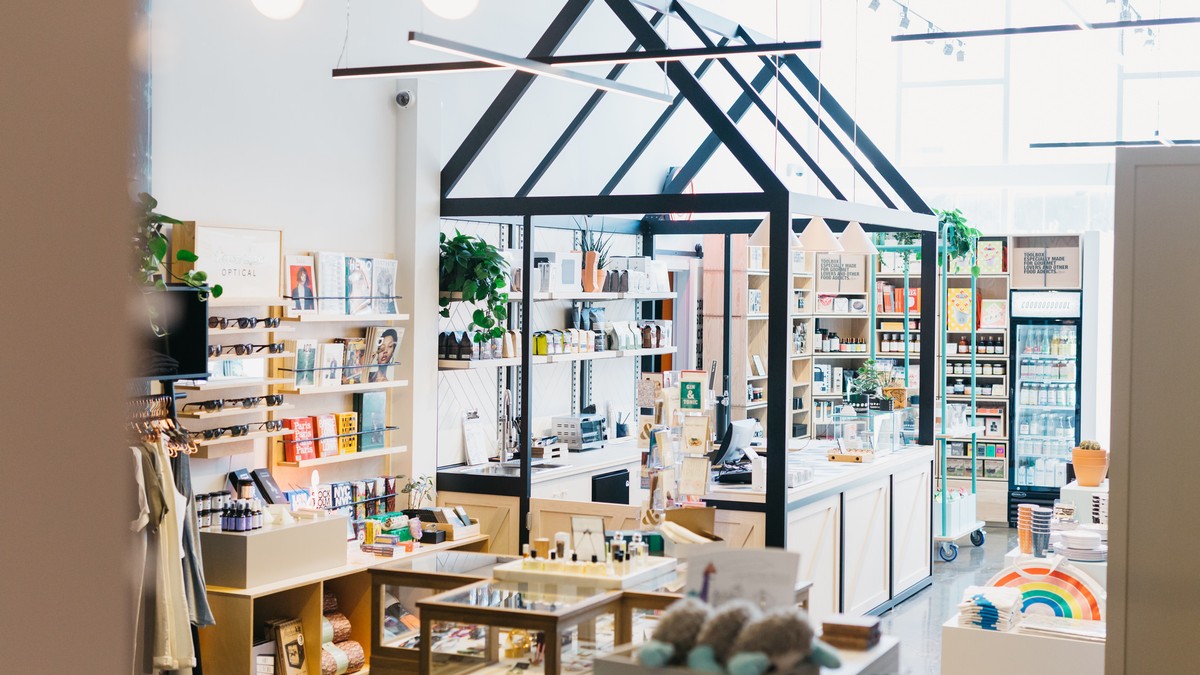
The Toronto-based startup’s origins lie in a Facebook group created by founder Emily Bitze in 2013. It began as an insider-y scene of young people bartering used stuff—the cardinal rule was “no money allowed in this zone.” The group soon exploded into having more than 60,000 members in the Toronto area alone, with spinoffs in numerous cities.
Bunz was a critical entry point for many newcomers to a secondhand market for furniture, knick-knacks, food, and whatever else. People made friends, found housing, and formed bands through the Facebook group and its many offshoots.
Apr. 19, 2018

He brought it to the attention of the manager, who promptly evacuated the 24-hour gym and called police. According to Saginaw Township Police Chief Donald Pussehl, a bomb-sniffing dog made a sweep of the premises, but it didn’t turn up any explosives.
Source: sophos.com
Apr. 19, 2018

To address this type of attacker, we present Oblivious DNS (ODNS), which is a new design of the DNS ecosystem that allows current DNS servers to remain unchanged and increases privacy for data in motion and at rest. In the ODNS system, both the client is modified with a local resolver, and there is a new authoritative name server for .odns. To prevent an eavesdropper from learning information, the DNS query must be encrypted; the client generates a request for www.foo.com , generates a session key k, encrypts the requested domain, and appends the TLD domain .odns, resulting in {www.foo.com}k.odns.
Apr. 19, 2018
T-Mobile admitted its deceptive scheme to the commission and received a $40 million fine. Given that the trick affected “hundreds of millions” of people in rural areas and perhaps billions of calls, the fine represents just a few cents per call. Even worse: Consumers will not see a cent for this deception that.
According to Ars Technica,FCC Commissioner Mignon Clyburn–who just stepped down from her post–was deeply critical of the fine, calling it absurdly low. The compliance plan contained in the FCC ruling, she says, “does not contain any concessions that would explain such a massive discount.” With Trump-appointed Ajit Pai in charge of the FCC, the treatment of telecomm companies probably won’t change any time soon.
Apr. 19, 2018

According to the PageFair 2014 report, Google Chrome is a major driver of adblock growth. 20% of users discovered ad blocking by browsing “available browser extensions”. Given how popular ad blocking is, it is quite a lot.
This also explains why ‘cloning’ wide-spread ad blockers has become so popular among online crooks. Seven months ago big news broke: 37,000 users were tricked into installing a fake Adblock Plus extension.
Apr. 19, 2018
Hackers initially got onto Piriform’s London networks by using stolen credentials to log into a TeamViewer remote desktop account on a developer PC. From there, the attackers moved laterally to a second computer, always working outside office hours when it was unlikely that people would be using the machines. The attackers installed malware called ShadowPad, sort of customizable malware platform that can be used for an assortment of attacks from DDoS to keylogging, on the compromised computers.
Apr. 18, 2018

Millions of apps leak personal identifiable information such as name, age, income and possibly even phone numbers and email addresses. At fault are app developers who do not protect ad-targeting data transmitted to third-party advertisers.
Source: threatpost.com
Apr. 18, 2018

This is an explanation of the key function on Proof-of-Work in the Bitcoin blockchain. It focuses on the one feature of Proof-of-Work that is essential and shows that other features often talked about such as security are secondary side-effects, useful, but not essential.
Source: grisha.org
Apr. 18, 2018
As Reuters reports, the lawsuit alleges that Facebook improperly collected and stored users’ biometric data. It was originally filed in 2015 by Facebook users in Illinois, which passed the Biometric Information Privacy Act (BIPA) in 2008. The law regulates the collection and storage of biometric data, and requires that a company receive an individual’s consent before it obtains their information.
Apr. 18, 2018

The GandCrab ransomware is reaching far and wide via malspam, social engineering schemes, and exploit kit campaigns. On April 16, we discovered that Magnitude EK, whichhad been loyal to its own Magniber ransomware, was now being leveraged to push out GandCrab, too.
Source: malwarebytes.com
Apr. 18, 2018
Global chip-maker Intel on Tuesday announced two new technologies—Threat Detection Technology (TDT) and Security Essentials—that not only offer hardware-based built-in security features across Intel processors but also improve threat detection without compromising system performance. Intel’s Threat Detection Technology (TDT) offers a new set of features that leverage hardware-level telemetry to help security products detect new classes of threats and exploits. It includes two main capabilities—Accelerated Memory Scanning and Advanced Platform Telemetry.