Mar. 16, 2018

It’s at least the second time in two years that Google has served up a malicious ad under Amazon’s name. Over the past year, we’ve heard of several cases of bad ads that have redirected users to malicious pages, but to our knowledge have never directly served malware.
Source: zdnet.com
Mar. 16, 2018
Throughout last year, mysterious ailments struck dozens of U.S. andCanadian diplomats and their families living in Cuba. Symptoms includeddizziness, sleeplessness, headache, and hearing loss; many of the afflictedwere in their homes or in hotel rooms when theyheard intense, high-pitched sounds shortly before falling ill. In February, neurologists who examined the diplomats concluded that the symptoms were consistent with concussion, but without any blunt trauma to the head.
Mar. 16, 2018

For those behind GandCrab, staying profitable and staying one-step ahead of white hats means adopting a never-before-seen agile malware development approach, said Check Point.
Source: threatpost.com
Mar. 16, 2018
Security researchers have discovered a massive continuously growing malware campaign that has already infected nearly 5 million mobile devices worldwide. Dubbed RottenSys, the malware that disguised as a ‘System Wi-Fi service’ app came pre-installed on millions of brand new smartphones manufactured by Honor, Huawei, Xiaomi, OPPO, Vivo, Samsung and GIONEE—added somewhere along the supply chain. All these affected devices were shipped through Tian Pai, a Hangzhou-based mobile phone distributor, but researchers are not sure if the company has direct involvement in this campaign.
Mar. 16, 2018

Researchers say a massive phishing campaign targeting Asia and Middle East regions is linked to an Iranian-based threat actorTEMP.Zagros, also known as MuddyWater. This latest attack illustrates an evolution by the threat actor, which has now adopted new tactics, techniques and procedures.
Source: threatpost.com
Mar. 16, 2018

This new backdoor for cross-border data mirrors another backdoor under Section 702 of the FISA Amendments Act, an invasive NSA surveillance authority for foreign intelligence gathering. That law, recently reauthorized and expanded by Congress for another six years, gives U.S. intelligence agencies, including the NSA, FBI, and CIA, the ability to search, read, and share our private electronic messages without first obtaining a warrant.
Mar. 16, 2018

Martisevs’ service was designed to keep new malware out of the hands of anti-virus makers. It didn’t report the detection of malicious files, thereby keeping anti-virus makers in the dark about new threats. The service had quite the palate: malware submitted to it included, among other types, crypters meant to hide malware from anti-virus programs, remote-access Trojans (RATs), keyloggers, and malware tool kits to create customized malicious files.
Mar. 16, 2018
A recent malware campaign that attempted to install a resource-draining currency miner on more than 400,000 computers in 12 hours was caused by a malicious backdoor that was sneaked into a BitTorrent application called Mediaget, a Microsoft researcher said Tuesday.
Source: arstechnica.com
Mar. 16, 2018

In August, a petrochemical company with a plant in Saudi Arabia was hit by a new kind of cyberassault. The attack was not designed to simply destroy data or shut down the plant, investigators believe. It was meant to sabotage the firm’s operations and trigger an explosion.
Source: nytimes.com
Mar. 16, 2018

The EU is considering a copyright proposal that would require code-sharing platforms to monitor all content that users upload for potential copyright infringement (see the EU Commission’s proposed Article 13 of the Copyright Directive). The proposal is aimed at music and videos on streaming platforms, based on a theory of a “value gap” between the profits those platforms make from uploaded works and what copyright holders of some uploaded works receive. However, the way it’s written captures many other types of content, including code.
Mar. 16, 2018
The only tools you need are at least one finger–a nose will work too–to type the brand and model of whatever device you want to hack, and a connected web browser. Put that information into a Google search box and, within a few minutes, you will find a site or a forum post somewhere describing how to enter into that device using the manufacturer’s default administration user name and password. Any pedophile, thief, ex-spouse, or regular Peeping Tom can use this information to gain access to any of these devices installed in your home.
Mar. 16, 2018

It’s hardly a secret that enterprises based in large emerging markets are clamoring to invest directly in U.S. companies—as well as in companies based in other advanced countries with hospitable economic environments—particularly through the acquisition of existing businesses. Foreign direct investment (FDI)—the ownership or control by a foreign entity of 10 percent or more of a domestic enterprise—plays a modest but growing role in the U.S. economy.
Mar. 15, 2018

Traffic distribution systems act as brokers that both buy and sell traffic from one site to another. They ad value by filtering traffic based on a user’s browser, IP address, geography anduser agent data. When a user clicks on a link that is part of a TDS chain they aresilently redirected to a malicious web pagebased on their profile.
TDS systems are notorious for aiding criminals in distributing web-based malware via exploit kits and fake downloads.
Mar. 15, 2018

Late last summer, I ‘Googled’ my regular diner to confirm its closing time, and was shocked to find that the site had marked it Permanently Closed. I quickly called the restaurant and learned, thankfully, that it hadn’t shut down; however, its Google presence had been hijacked. And
despite the owners’ best efforts
Source: forbes.com
Mar. 14, 2018
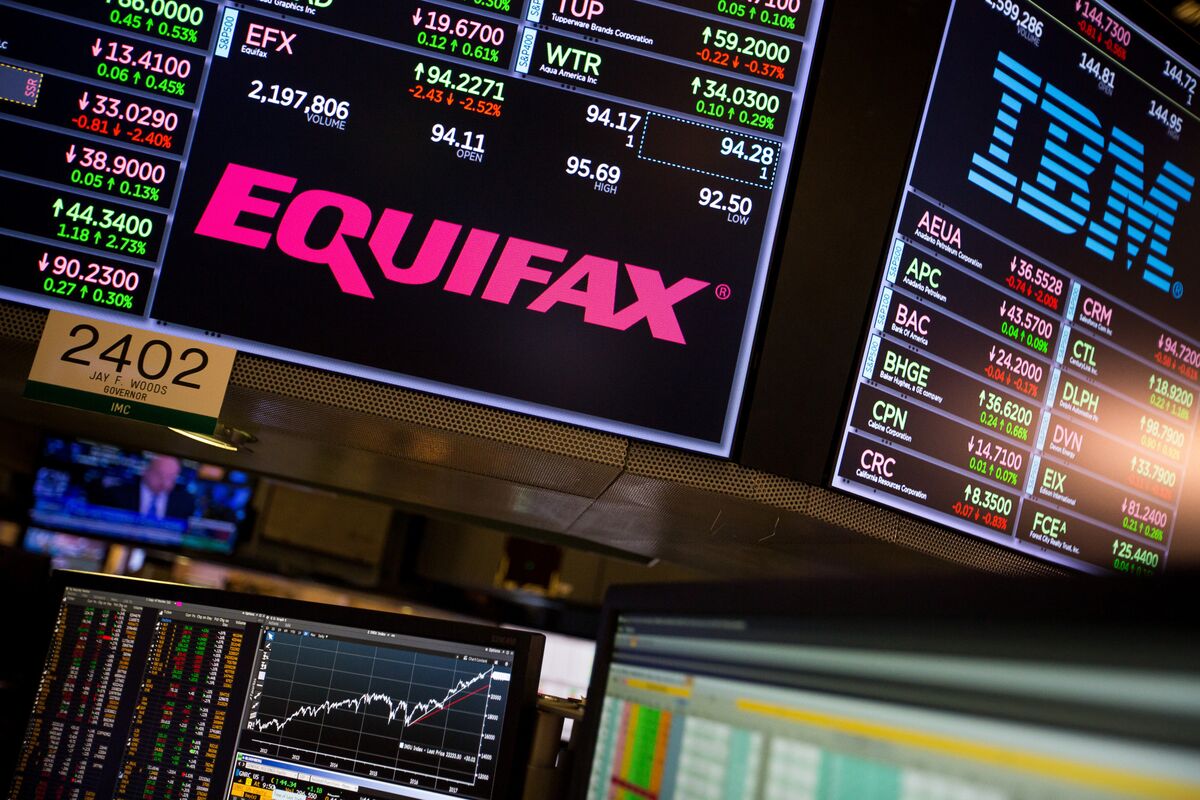
Six months after the cyberattack shook Equifax and raised questions about suspicious trading by several executives there, the Department of Justice on Wednesday charged Ying with insider trading. Prosecutors say he searched on the internet for what might happen to Equifax stock when the news of the attack broke, then exercised all of his stock options. The move netted him more than $480,000.
Mar. 14, 2018

Researchers at Kroll Cyber Security first identified PinkKite in 2017 during a nine-month investigation into a large POS malware campaign that ended in December. The campaign is believed to be the first instance of PinkKite identified, according to researchers Courtney Dayter and Matt Bromiley, who presented their findings at Kaspersky Lab’s Security Analyst Summit on Friday.
Source: threatpost.com
Mar. 14, 2018
One of the biggest campaign operators using Coinhive—an in-browser cryptocurrency mining service—made a measly $7.69 USD after running Coinhive’s script on 11,000 websites for three months, according to a new report published to arXiv last week.
Source: vice.com
Mar. 14, 2018

How to deal with rootkit analysis step by step: laboratory setup, Windows kernel architecture and API, Windows protection, Windows 10 64 bits
Source: sekoia.fr
Mar. 14, 2018

There are roots in legitimacy here, but as we dug deep into the origins of the companies involved in this new hit piece on AMD, we found peculiar financial connections that make us question the motive behind the reportage.
Source: gamersnexus.net