Mar. 13, 2018
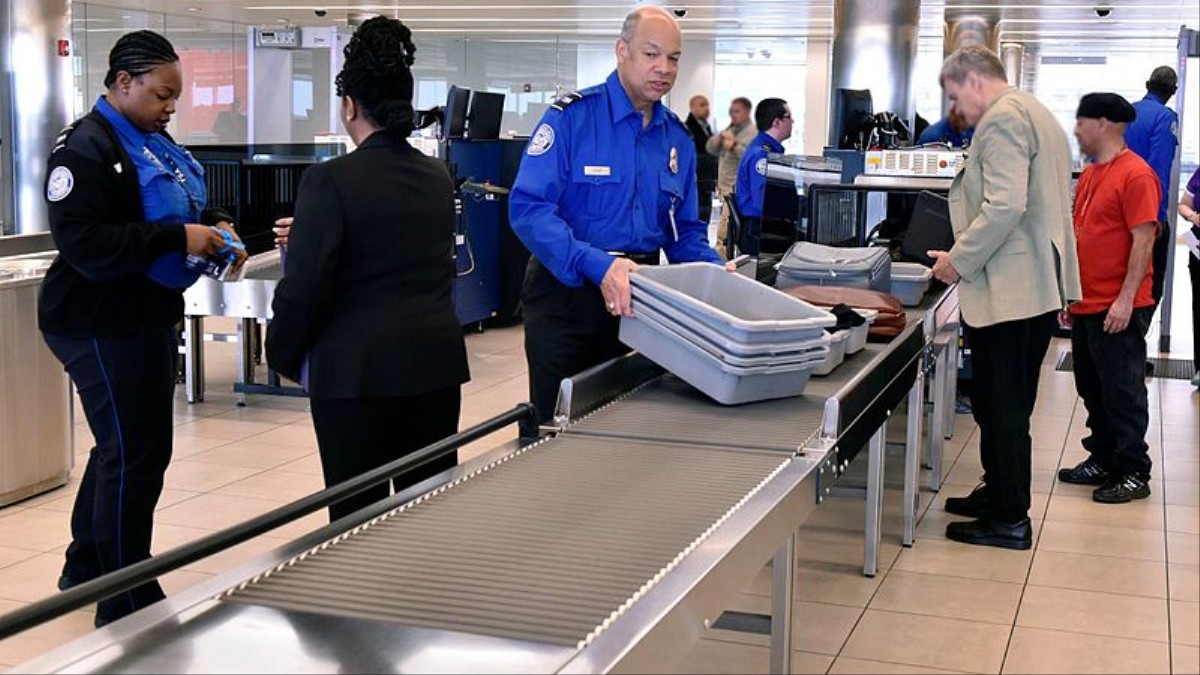
Flying sucks enough as it is, but a Transportation Security Administration employee deciding to root around in your laptop or cellphone can make it even worse. This practice of searching electronic devices has been going on for years at international airports, but this was limited to travelers flying in and out of the US. Recently there has a large uptick in the number of devices searched by Customs and Border Protection agents: Last year, CBP officials searched 30,000 devices, up from just 5,000 in 2015.
Mar. 13, 2018
This utility, going by the codename of ‘Territorial Dispute,’ is meant to alert NSA operators about the presence of other cyber-espionage hacking groups on a compromised computer and allows an NSA operator to retreat from an infected machine and avoid further exposure of NSA hacking tools and operations to other nation-state attackers.
Source: bleepingcomputer.com
Mar. 13, 2018

Some readers may remember our Analysis of .git folders in the Alexa Top 1M. WIth our tools we were able to discover and retrieve (hidden) directories and files (even without directory listing). We developed a similar approach of uncovering hidden files again, but this time with the help of .DS_Store files. In this blogpost we will share the methodology, the resulting security implications as well as our results from scanning the Alexa Top 1M and how we could have obtained sensitive files from several websites.
Mar. 13, 2018

Microarchitectural attacks can also be implemented in JavaScript, exploiting properties inherent to the design of the microarchitecture, such as timing differences in memory accesses. Although JavaScript code runs in a sandbox, Oren et al. demonstrated that it is possible to mount cache attacks in JavaScript. Since their work, a series of microarchitectural attacks have been mounted from websites, such as page deduplication attacks, Rowhammer attacks, ASLR bypasses, and DRAM addressing attacks.
Mar. 13, 2018
Amazon as a Tech company and everything store, is perhaps the only thing Millennials trust more than investing in cryptocurrencies. We’ve now reached a point where Big Tech will race to adopt them and it could change the future of banking and payments.
Source: medium.com
Mar. 13, 2018
Last week, the Frankfurt School of Finance & Management hosted CryptoTax for a seminar on the German taxation regime. The webinar recording is available on YouTube (in German only), and the key points have been summarized here for the benefit of a global audience.
Source: medium.com
Mar. 13, 2018
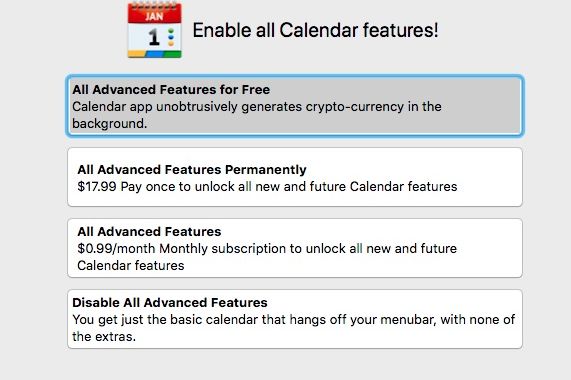
Resource-draining currency miners are a regular part of the Google Play market, as scammers pump out apps that covertly harness millions of devices, in some cases with malware so aggressive it can physically damage phones. A popular title in the Mac App Store recently embraced coin mining openly, and so far Apple gatekeepers haven’t blocked it.
Mar. 13, 2018

It all started with the public disclosure of a HackerOne report submitted to Keybase by another researcher. It was a minor character escaping issue, but one that probably had the highest impact of all vulnerability reports submitted to their program—given that it was issued their highest bounty payout at the time. I immediately noticed the ‘patch’ they implemented was insufficient, and it was only a matter of minutes before I submitted a new vulnerability report (as quickly and as fast as possible).
Mar. 13, 2018
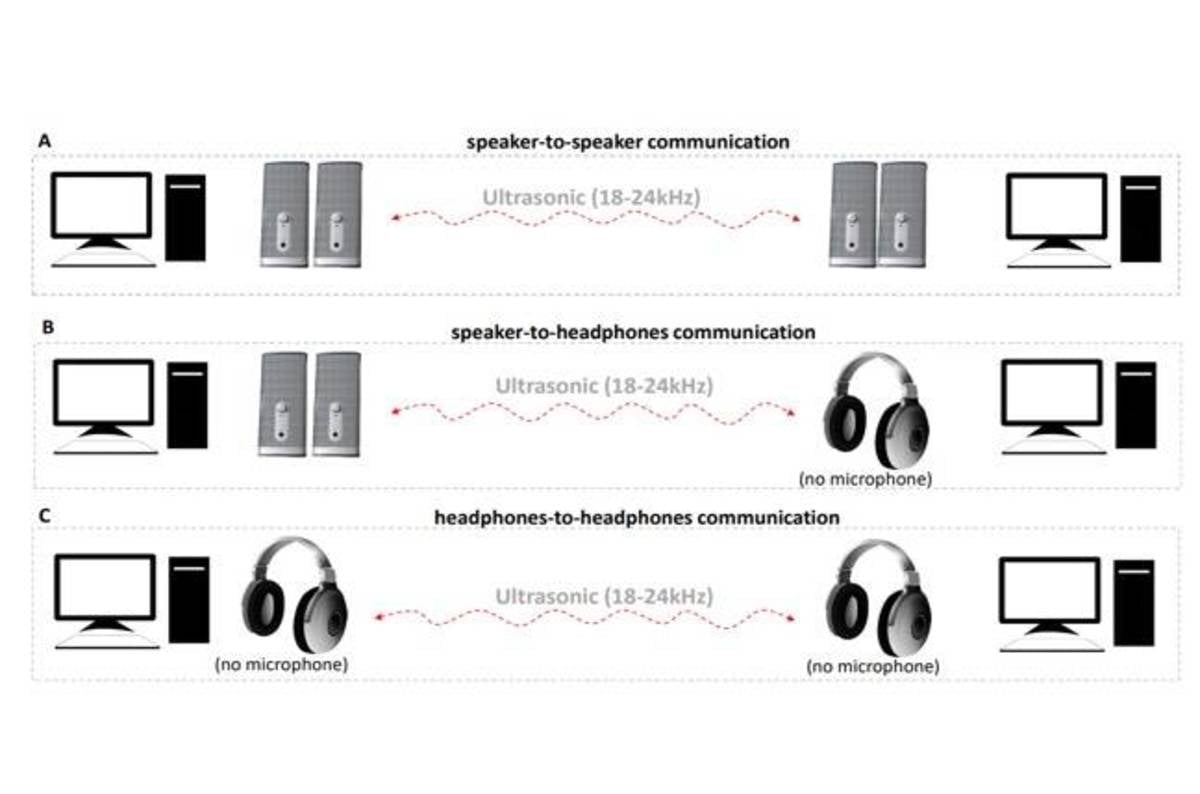
In an academic paper published on Friday through preprint service ArXiv, researchers from Israel’s Ben-Gurion University of the Negev describe a novel data exfiltration technique that allows the transmission and reception of data – in the form of inaudible ultrasonic sound waves – between two computers in the same room without microphones.
Source: co.uk
Mar. 13, 2018
There are a growing number of reports of the Transportation Security Administration (TSA) searching the electronic devices of passengers on domestic flights in the US, according to the American Civil Liberties Union (ACLU), which has sued the federal agency for records. The ACLU Foundation of Northern California filed a lawsuit against the TSA on Monday demanding that the government disclose its policies for searching the computers and cellphones of domestic travelers, arguing that anecdotal accounts have raised concerns about potential privacy invasions.
Mar. 13, 2018
The team of security researchers—who last month demonstrated how attackers could steal data from air-gapped computers protected inside a Faraday cage—are back with its new research showing how two (or more) air-gapped PCs placed in the same room can covertly exchange data via ultrasonic waves. Air-gapped computers are believed to be the most secure setup wherein the systems remain isolated from the Internet and local networks, requiring physical access to access data via a USB flash drive or other removable media. Dubbed MOSQUITO, the new technique, discovered by a team of researchers at Israel’s Ben Gurion University, works by reversing connected speakers (passive speakers, headphones, or earphones) into microphones by exploiting a specific audio chip feature.
Mar. 13, 2018

Yahoo has been ordered by a federal judge to face much of a lawsuit in the United States claiming that the personal information of all 3 billion users was compromised in a series of data breaches.
Source: reuters.com
Mar. 12, 2018
In November 2017, Recorded Future published research examining the publication speed for China’s National Vulnerability Database (CNNVD). While conducting that research, we discovered that China had a process for evaluating whether high-threat vulnerabilities had operational utility in intelligence operations before publishing them to the CNNVD. In revisiting that analysis, we discovered that CNNVD had altered their initial vulnerability publication dates in what we assess is an attempt to cover up that evaluation process.
Mar. 12, 2018
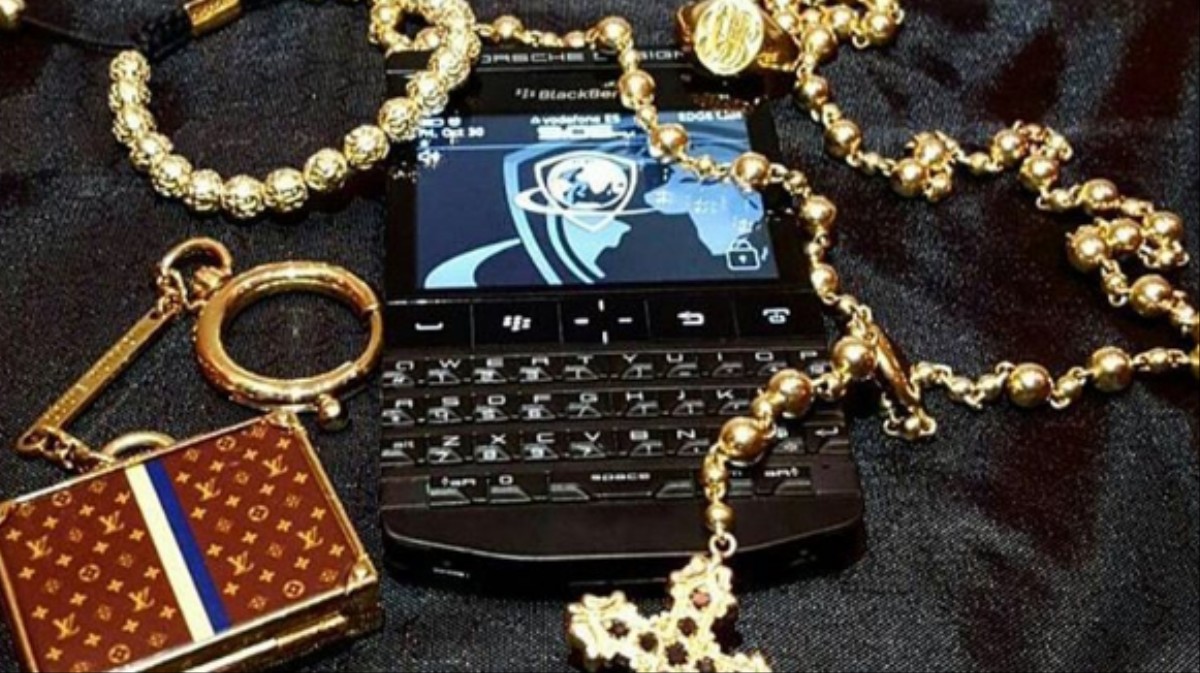
On Saturday, Motherboard reported that the FBI has arrested the CEO of Phantom Secure, a company allegedly providing security-focused phones to international organized crime groups including the Sinaloa drug cartel. A key issue is whether Phantom deliberately created its product to help facilitate crime, which the criminal complaint alleges.
Source: vice.com
Mar. 12, 2018
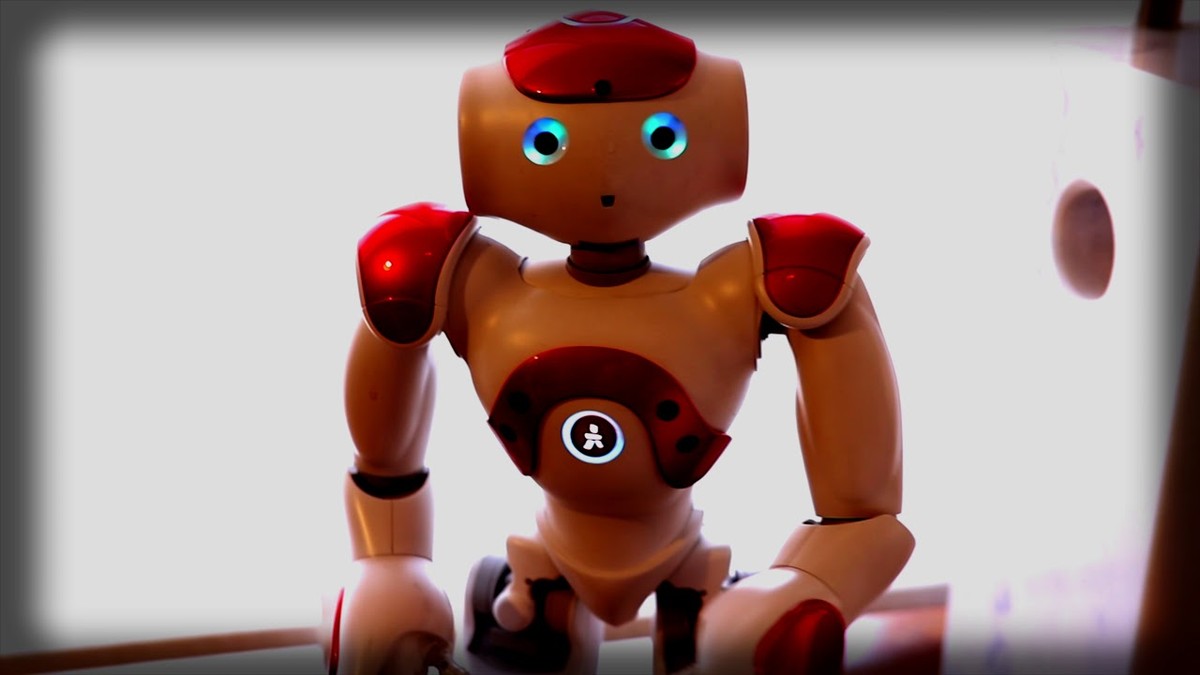
In their March 9 paper, “Robots want bitcoins too,” IOActive security researches Lucas Apa and Cesar Cerrudo successfully created ransomware that could be used to compromise SoftBank Robotics’ NAO robot. Unlike traditional computer ransomware which threatens customers by encrypting their personal information, in the situation presented by the researches, companies that rely on these robots for service would be forced to make a decision: pay the ransom or cease business.
Mar. 12, 2018

If you’re using JavaScript on the server side (node.js), then you’ll want to understand the class of vulnerabilities described in this paper. JavaScript on the server side doesn’t enjoy some of the same protections as JavaScript running in a browser. In particular, Node.js modules can interact freely with the operating system without the benefit of a security sandbox.
The bottom line is this:
Mar. 12, 2018

Around the globe, the region where criminals had achieved expertise and have become highly professionals is Latin America. As a resulting of this criminal union to steal money directly from ATM, criminals and cybercriminals from Latin America have been developing brand new zero-day techniques and tools that are not found in any other place in the world.
Source: securityaffairs.co
Mar. 12, 2018
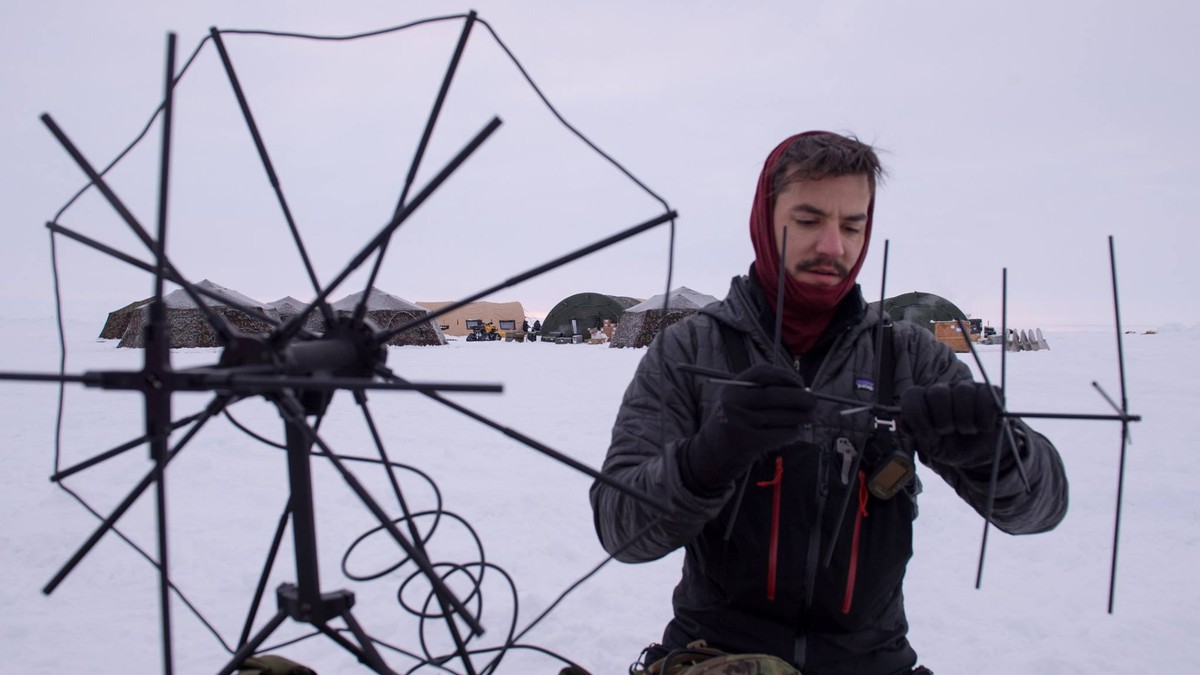
The US Navy submarines USS Connecticut and USS Hartford are meeting the British Royal Navy sub HMS Trenchant under an ice floe on the Arctic Sea. The subs, each with a crew of more than 100 sailors, combined are bringing along scores of researchers from government agencies and universities.
Source: vice.com
Mar. 12, 2018

The researchers at Kaspersky Lab ICS CERT decided to check the popular smart camera to see how well protected it is against cyber abuses. This model has a rich feature list, compares favorably to regular webcams and can be used as a baby monitor, a component in a home security system or as part of a monitoring system.
Source: securelist.com
Mar. 12, 2018

DJI drones have been on the radar of the hacker community for quite a long time. The interest of its members revolves mostly around unblocking some features of drones, setting control channels of drones to a higher frequency, and removing such restrictions as flight altitude limits or strictly set no-fly zones. Moreover, there are piles of publicly available info about jailbreaking drones.
The most useful know-hows produced by the community are gathered in several Github cross-referenced repositories. Those striving for knowledge may also check the community wiki dji.retroroms.info. For quite a while the website has been accessible as a web archive only, but now the wiki is available again.