Oct. 27, 2018

A software security engineer has identified 12 Python libraries uploaded on the official Python Package Index (PyPI) that contained malicious code. The 12 packages have been discovered in two separate scans by a security engineer who goes online by the name of Bertus, and have long been removed from PyPI before this article’s publication. All packages were put together and worked following a similar pattern.
Oct. 26, 2018

A deeper investigation has revealed that hackers were stealing information for much longer than initially thought, and an additional 185,000 British Airways customer payment cards were compromised. Last month, British Airways announced that the customer data and details of some 380,000 card payments had been stolen from its network by hackers between August 21 and September 5 2018. Now, in an update posted on its website, British Airways says it has discovered that more of its customers have been affected – with potentially impacted individuals being those who made reward bookings between April 21 and July 28, 2018, and who used a payment card.
Oct. 26, 2018
Several big-name Linux and BSD operating systems are vulnerable to an exploit that gives untrusted users powerful root privileges. The critical flaw in the X.org server—the open-source implementation of the X11 system that helps manage graphics displays—affects OpenBSD, widely considered to be among the most secure OSes. It also impacts some versions of the Red Hat, Ubuntu, Debian, and CentOS distributions of Linux.
Oct. 4, 2018

In 2015, Amazon.com Inc. began quietly evaluating a startup called Elemental Technologies, a potential acquisition to help with a major expansion of its streaming video service, known today as Amazon Prime Video. Based in Portland, Ore., Elemental made software for compressing massive video files and formatting them for different devices. Its technology had helped stream the Olympic Games online, communicate with the International Space Station, and funnel drone footage to the Central Intelligence Agency.
Oct. 1, 2018
The Facebook hack is even worse than was at first clear, the company has admitted. The site had already admitted that a hole in its code would allow people to gain access to any account, in a problem that affected some 50 million users. But it later said that the problem would also affect its ‘Facebook Login’ service, which allows other apps to use people’s Facebook account to login.
Sep. 30, 2018
Nearly 50m Facebook accounts were compromised by an attack that gave hackers the ability to take over users’ accounts, Facebook revealed on Friday. The breach was discovered by Facebook engineers on Tuesday 25 September, the company said, and patched on Thursday. Users whose accounts were affected will be notified by Facebook.
Those users will be logged out of their accounts and required to log back in. The security breach is believed to be the largest in Facebook’s history and is particularly severe because the attackers stole “access tokens”, a kind of security key that allows users to stay logged into Facebook over multiple browsing sessions without entering their password every time. Possessing a token allows an attacker to take full control of the victim’s account, including logging into third-party applications that use Facebook Login.
Sep. 29, 2018
This morning, news broke that a massive data breach has exposed the personal information of 50 million Facebook users to hackers. A company blog reports that nearly 90 million users were forced to log out out of their accounts as a security precaution and provided little detail on what personal information attackers were able to access. Shortly after, reports began to circulate on Twitter that Facebook was blocking a Guardian story about the breach from being posted on its platform: Within minutes, additional reports began to circulate that an Associated Press story about the breach was being blocked as well: Internet users and journalists struggled to make sense of why Facebook was censoring this massive news story for over an hour until reports once again surfaced on Twitter suggesting that the block had been resolved: While it appears as though Facebookâs effort to block the story was an anti-SPAM glitch, itâs hard to imagine how this day could have gone much worse for Facebook.
Sep. 27, 2018
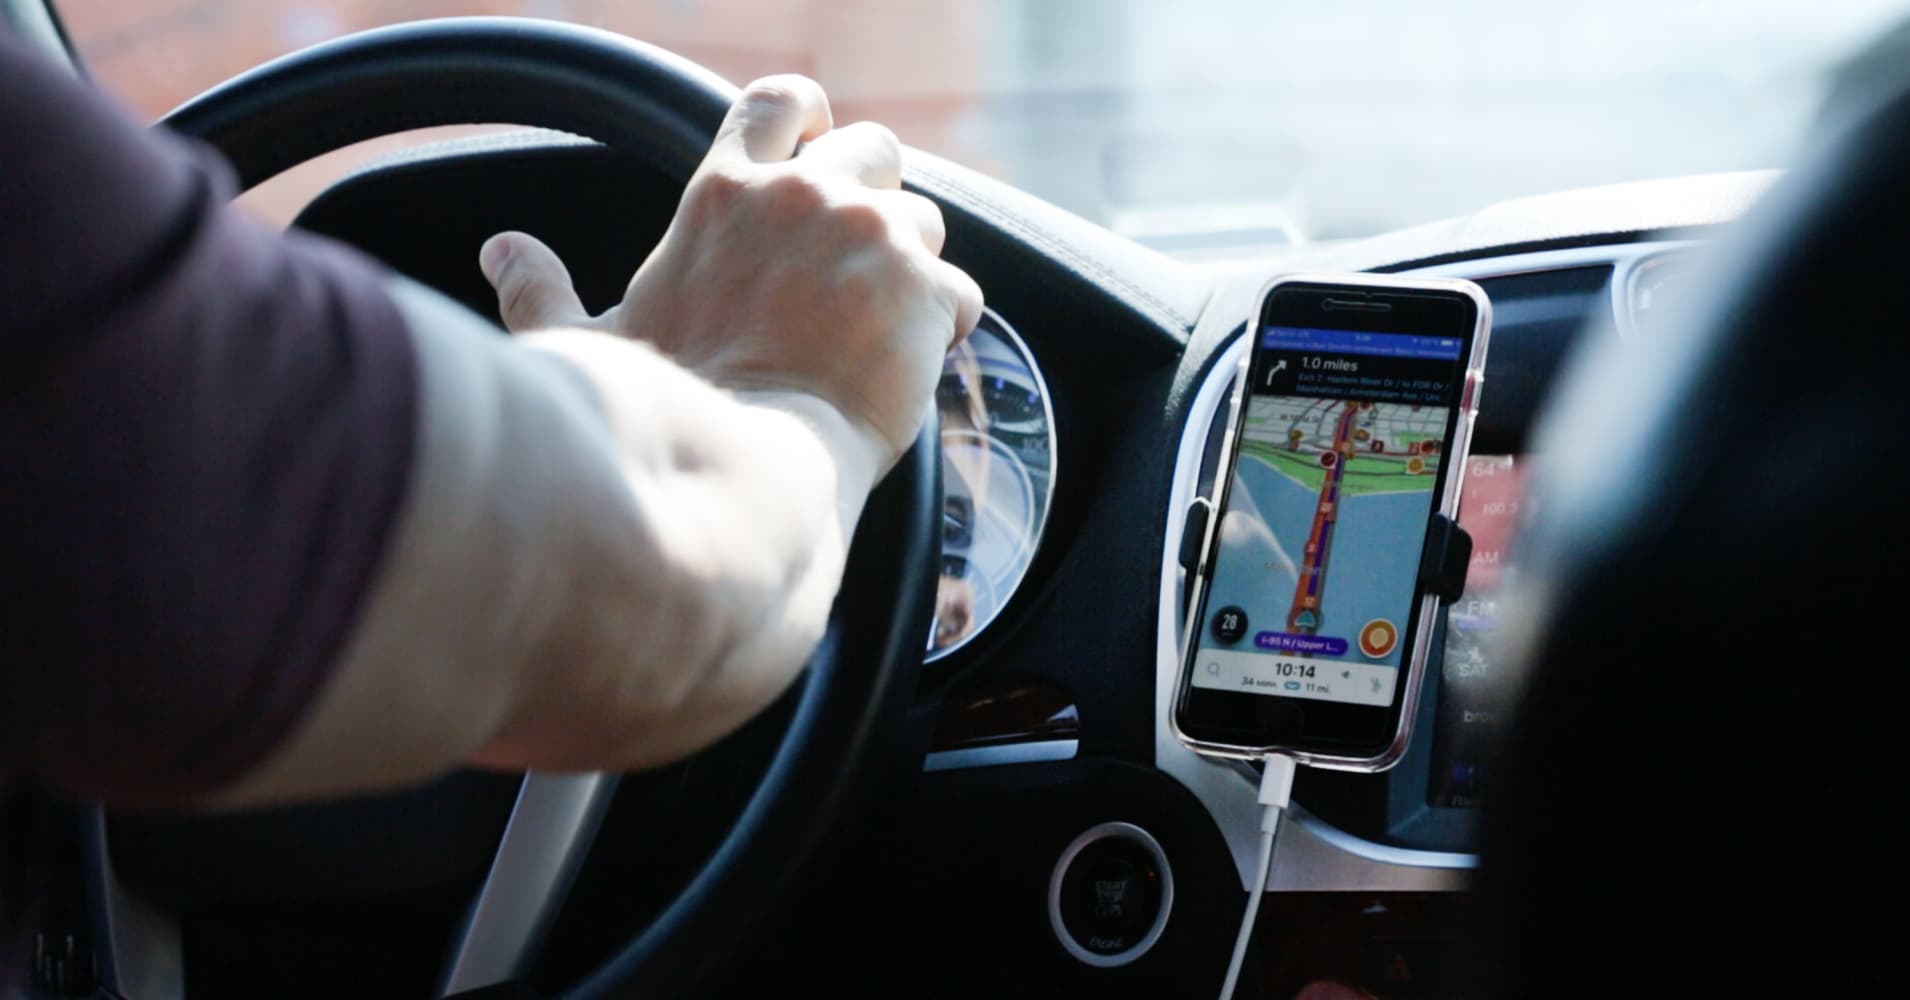
The breach, revealed last year, granted hackers access to the personal information of 57 million riders and drivers. Uber paid the hackers $100,000 to delete the data and keep the breach quiet, rather than report the incident. Uber has agreed to pay $148 million in connection with a 2016 data breach and subsequent cover-up, according to the California Attorney General’s office.
Sep. 27, 2018
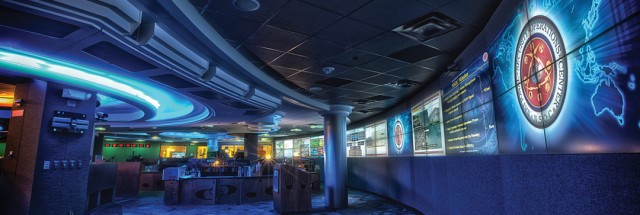
The National Security Operations Center at NSA, photographed in 2012—the nerve center of the NSA’s ‘signals intelligence’ monitoring. A former NSA coder has been sentenced to 66 months in prison for bringing home the code that drove much of the NSA’s signals intelligence operations. Nghia Hoang Pho, a 68-year-old former National Security Agency employee who worked in the NSA’s Tailored Access Operations (TAO) division, was sentenced today to 66 months in prison for willful, unauthorized removal and retention of classified documents and material from his workplace—material that included hacking tools that were likely part of the code dumped by the individual or group known as Shadowbrokers in the summer of 2016.
Sep. 25, 2018

As it has done with the issues of online privacy and restoring net neutrality, California becomes the first state to act to secure the Internet of Things. It’s back to the future time again for California. Having adopted the nation’s toughest online privacy protection measure and restored state-level net neutrality protections that are tougher on ISPs than the FCC regulations, the Golden State’s Legislature has just sent a bill to the governor’s desk for signature that would make California the first state to attempt IoT security governance.
Sep. 23, 2018

Earlier this week, a bug was found in the Bitcoin’s core code base. Developers got in the rush, and finally released a fix on Tuesday. The bug turned out to be Denial of Service bug (DoS).
Furthermore, if anyone exploited the vulnerability, this could be used to disconnect nodes, or even crash a whole segment of a network. This was enough to rush the developers into action. The bug could be exploited by any miner, to double spend any transaction.
Sep. 23, 2018

Starting with Chrome 69, logging into a Google Site is tied to logging into Chrome. This is typically the topic where things are complex enough that tweets or 500 character Mastodon toots don’t do it justice. I’d also mention that I prefer to avoid directly linking people’s posts on this, because I dislike the practice of taking discussions out of their original audience and treating them as official or semi-official communications from a given company.
Sep. 22, 2018
Six hundred microseconds. That is about the time that Matt Corallo wanted to shave off of block validation with his pull request in 2016 to Bitcoin Core. 600µs is a lot less than what is saved with more efficient block propagation, like XThin, Compact Blocks, or now Graphene over typical links, especially those that are of similar low-end quality in network speed like Raspberry Pis are in compute speed.
Sep. 21, 2018

Canadian retailer NCIX filed for bankruptcy and closed 10 months ago. They were the premiere PC hardware retail store in Canada and even did a sizable business on the other side of the border. However, as Travis Doering of Privacy Fly found out, the company did not go quietly away without doing some damage to their customer’s security first.
Doering recounts meeting up with a Craigslist seller claiming to have NCIX’ Database servers for only $1500 CAD. This includes a Database Server from NCIX and a Database Reporting Server, allegedly legally obtained via Able Auctions. Prior to NCIX shutting down, their assets were sold off through this company.
Sep. 20, 2018

In a major development, Japanese crypto exchange Zaif has been on the receiving end of a hacking incident last week, local media has reported. The hack, which occurred on Sept. 14 but was not discovered until Sept. 17, saw the hacker steal 4.5 billion yen from users hot wallets, as well as 2.2 billion yen from the assets of the company, with total losses amounting to 6.7 billion yen or around $59.7 million. Tech Bureau Inc. which operates the digital currency exchange Zaif said in a press release that the company noticed certain abnormalities on September 17, and the hacking damage was confirmed on September 18.
Sep. 20, 2018

While the dust is settling on the British Airways compromise, the Magecart actor behind it has not stopped their work, hitting yet another large merchant: Newegg. Last week we published details on the British Airways compromise immediately after the company made its first advisory public linking the breach of customer credit card information to Magecart. We were able to disclose these details based on our years of tracking the activities and infrastructure of the umbrella of Magecart groups performing digital credit card skimming campaigns.
Sep. 19, 2018
Over the last 24 hours, the cryptocurrency community has been discussing a critical vulnerability that was found in the Bitcoin Core (BTC) reference client. A bug introduced in Bitcoin Core version 0.14, that also affects all subsequent versions, could have caused a great majority of current Core nodes to crash. According to the developer’s Optech newsletter, Core contributors released a patch that fixes Core version 0.16.2 and the latest 0.16.3 fix requires an immediate upgrade.
Sep. 17, 2018

EOS has recently been in the news following the revelation that an EOS decentralized application (dApp) could access users’ token wallets without their consent through the use of a backdoor technique. More specifically, this EOS dApp is called Trybe, and describes itself as a ”tokenized knowledge sharing network for the crypto and blockchain community”. Issues first arose when Trybe were set to distribute tokens to user accounts through a token airdrop.
Sep. 17, 2018
Although more casual, less-technical crypto-enthusiasts might not know much on this topic, an essential aspect of any cryptocurrency project is the consensus algorithm that it utilizes. These algorithms accomplish two major objectives. Firstly, it ensures that the next block in a blockchain is the true, master-version of the details.
Secondly, it makes sure that those looking to take advantage of the system and fork the chain are stopped. Either way, the point is that consensus algorithms are the way that cryptocurrencies ensure that their digital tokens aren’t victim to double spending. While essential, there have emerged a wide variety of consensus algorithms amongst the various cryptocurrencies, each with their own pros and cons.
Sep. 17, 2018

The virtual machine that allows ethereum to compute everything in a decentralized way is getting a massive overhaul. At the heart of ethereum lies a virtual computer. Stored across tens of thousands of nodes that make up the platform, the ethereum virtual machine, or EVM, is responsible for executing the countless tokens,dapps, DAOs and digital kittens of which the blockchain is comprised of.